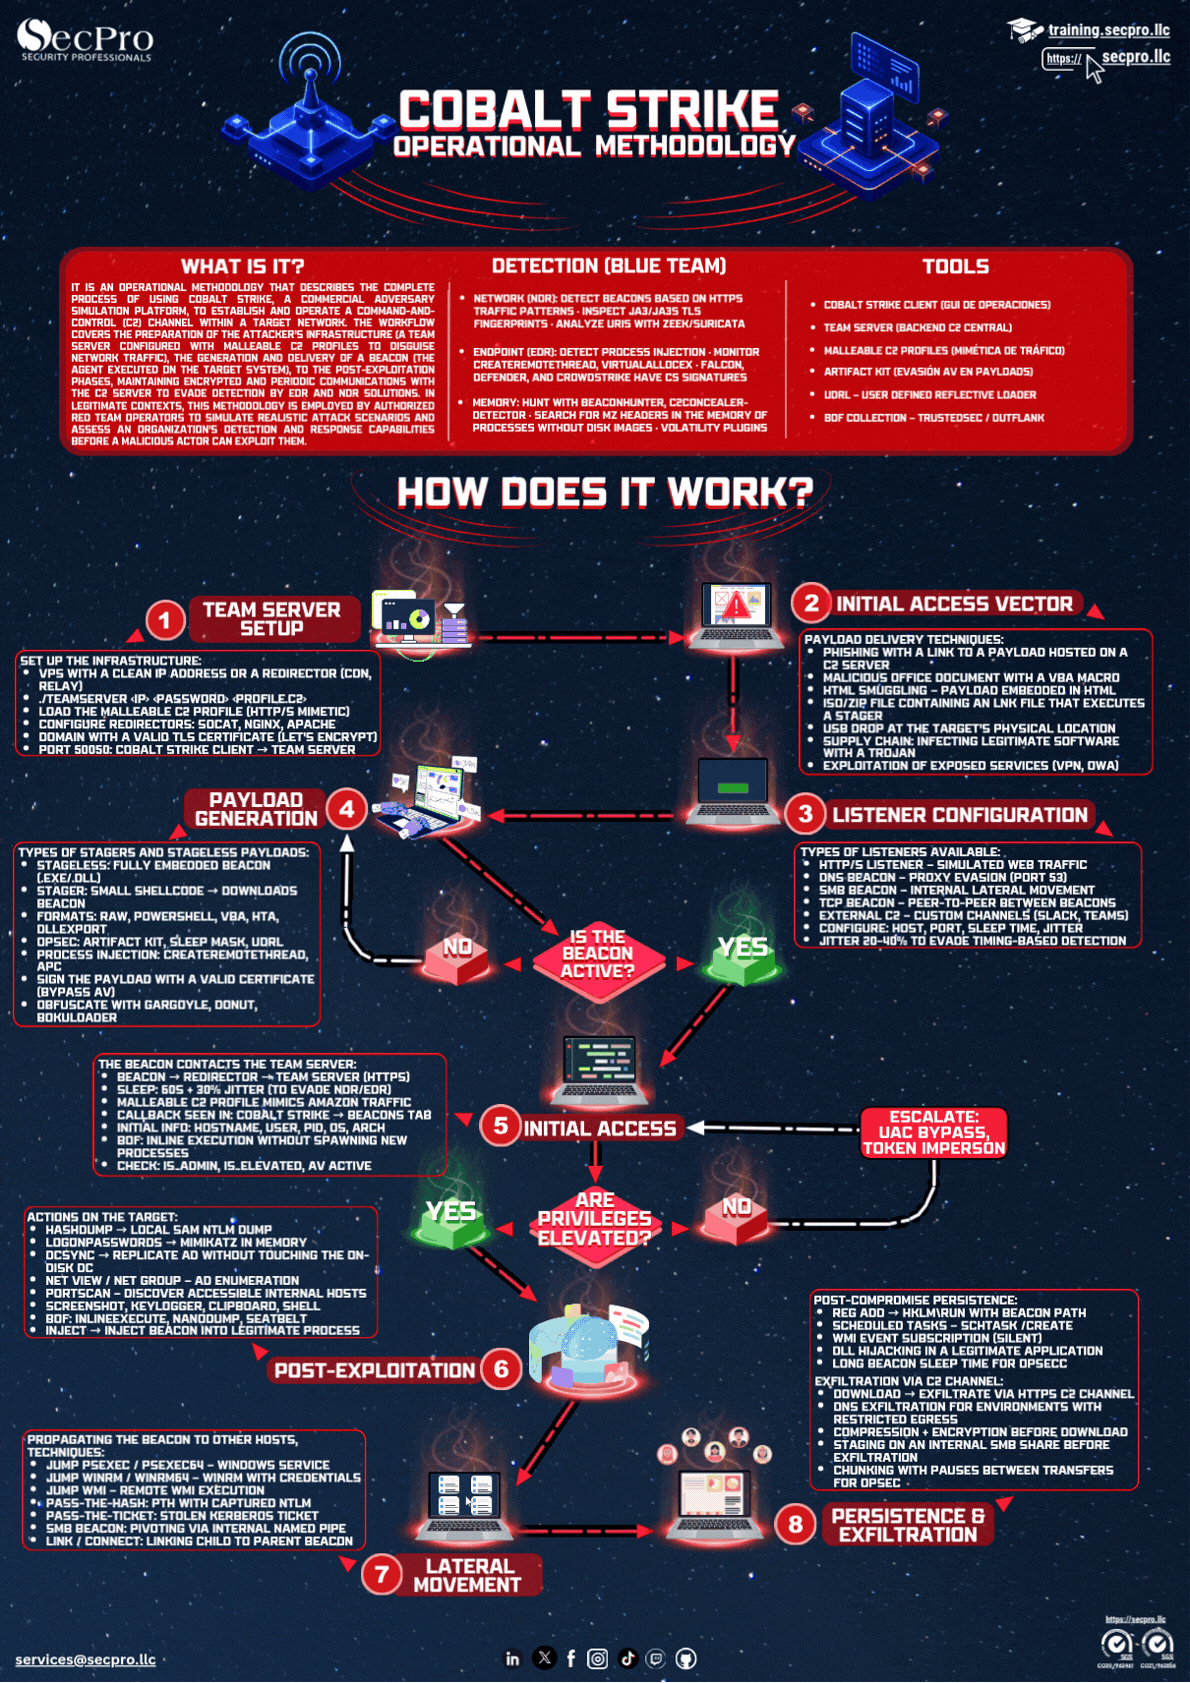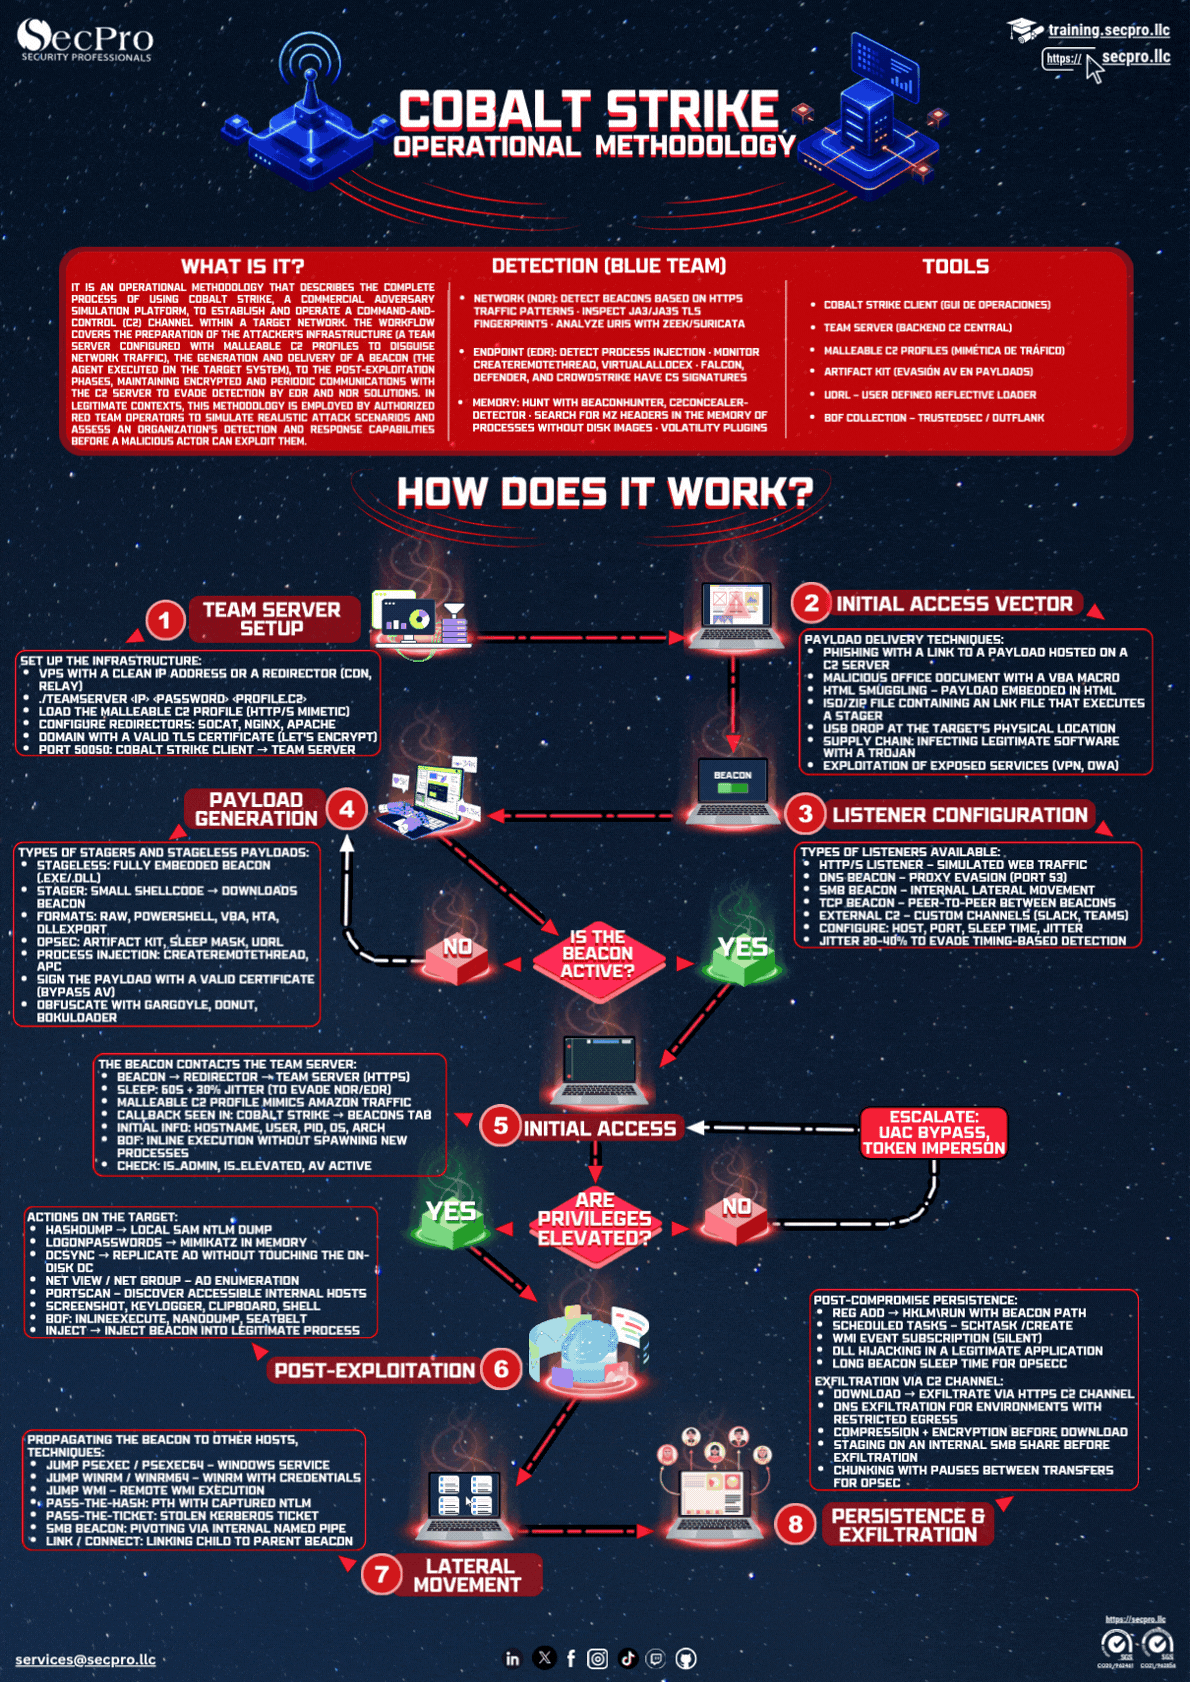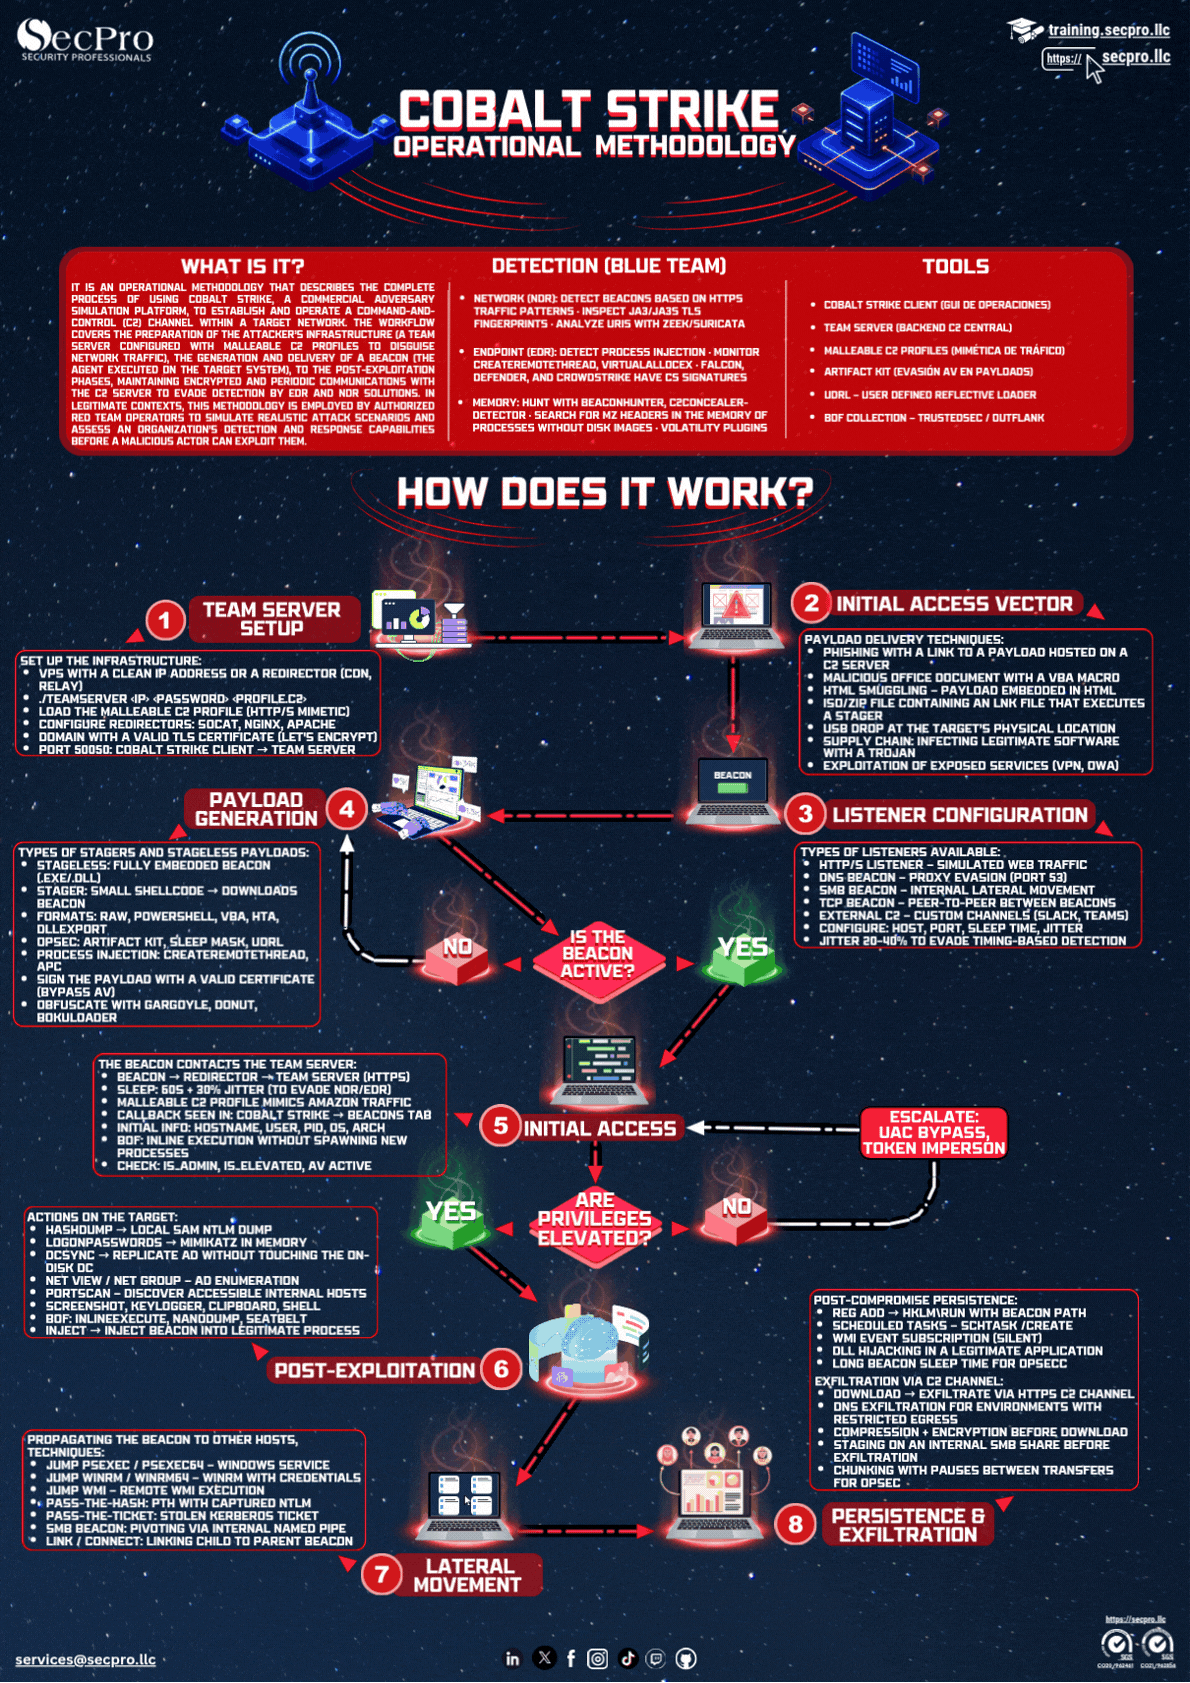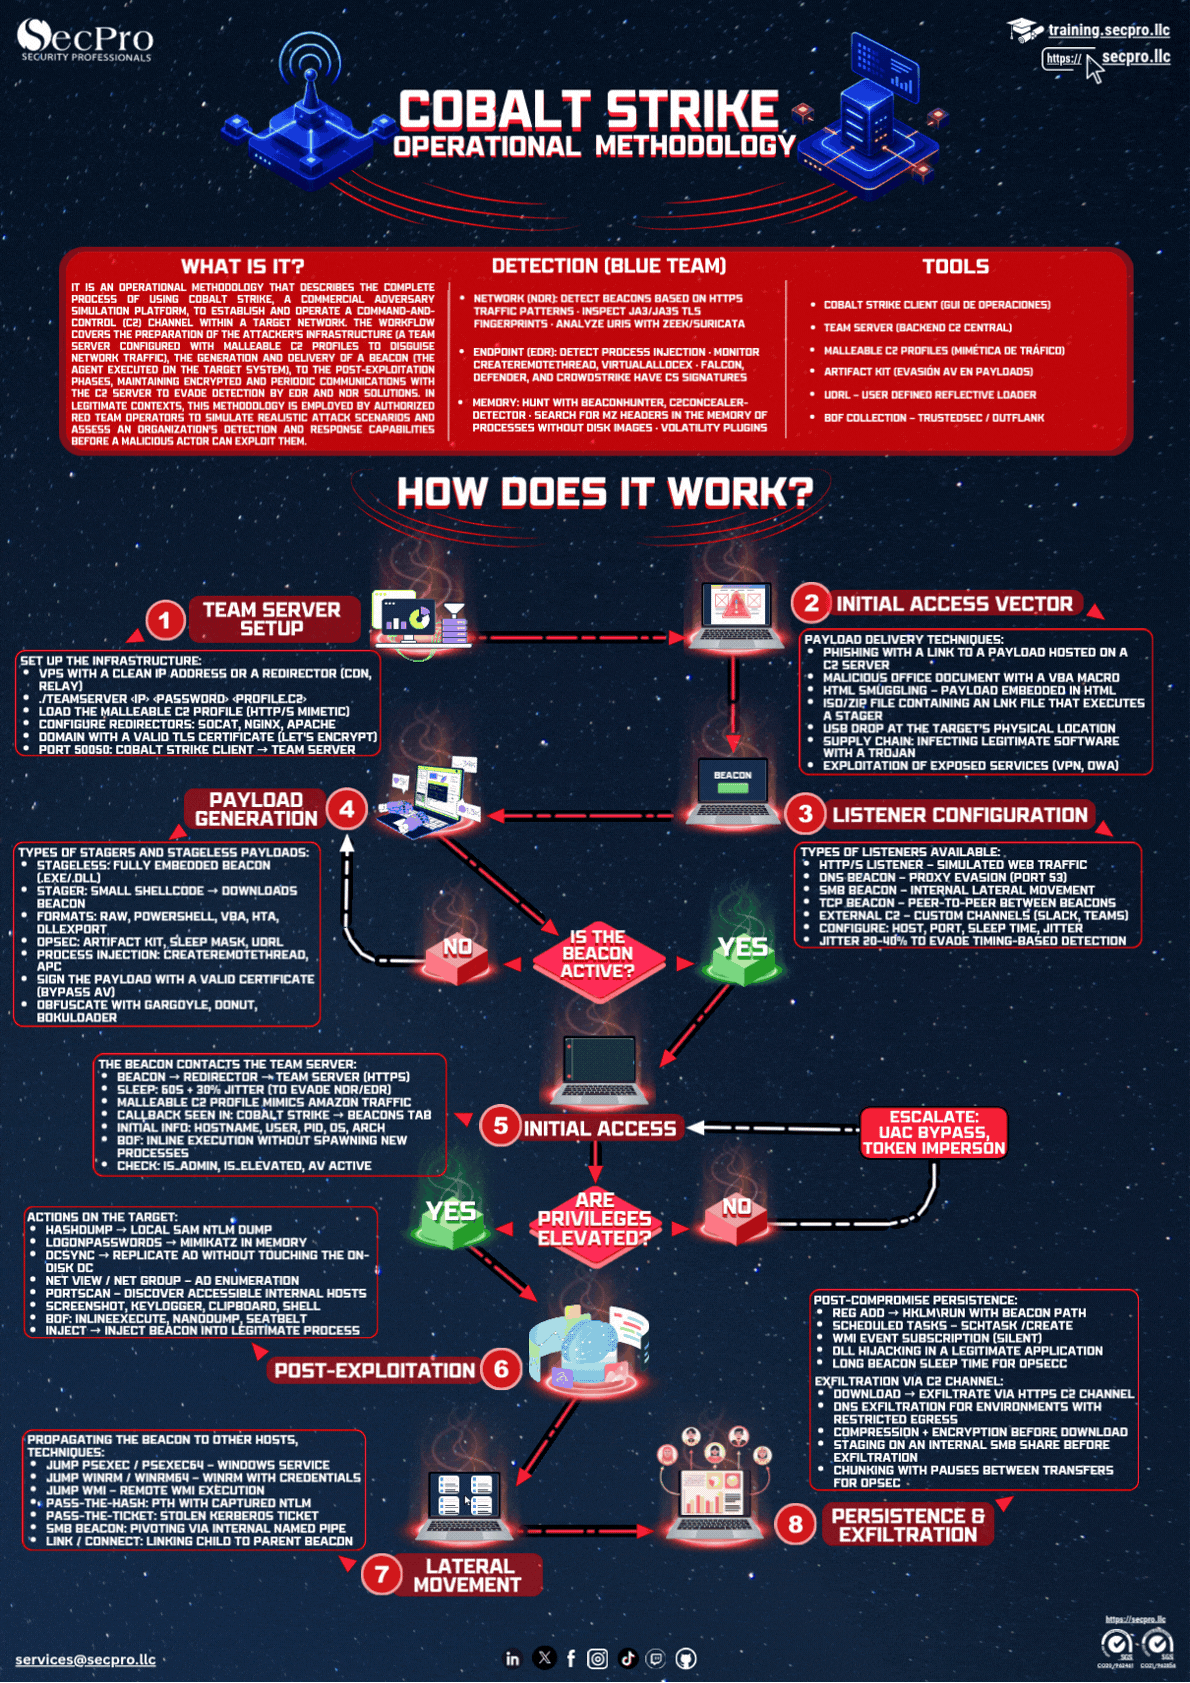
What is Cobalt Strike?
Cobalt Strike is a commercial adversary simulation platform: a command-and-control server with an implant called Beacon deployed on target machines. It was designed so Red Teams could reproduce, under control, what a real attacker does — persistence, lateral movement, credential theft, exfiltration — with traceability and under an agreed scope.
Why it shows up so often in real incidents
Because cracked versions have circulated for years and it saves criminal groups from developing their own tooling. Ransomware operators and intrusion groups use it routinely, to the point that for a defensive team finding a Beacon on their network is, statistically, far more likely to be a real attacker than an authorized exercise.
How is it detected?
By behavior rather than signature, because malleable profiles allow disguising traffic and changing static indicators. Useful signals are periodic beacons at regular intervals toward one destination — even with jitter, the pattern shows over long windows — injection into legitimate processes, named pipes used for internal communication, and default or reused TLS certificates. An honest exercise measures precisely whether the defender sees this.