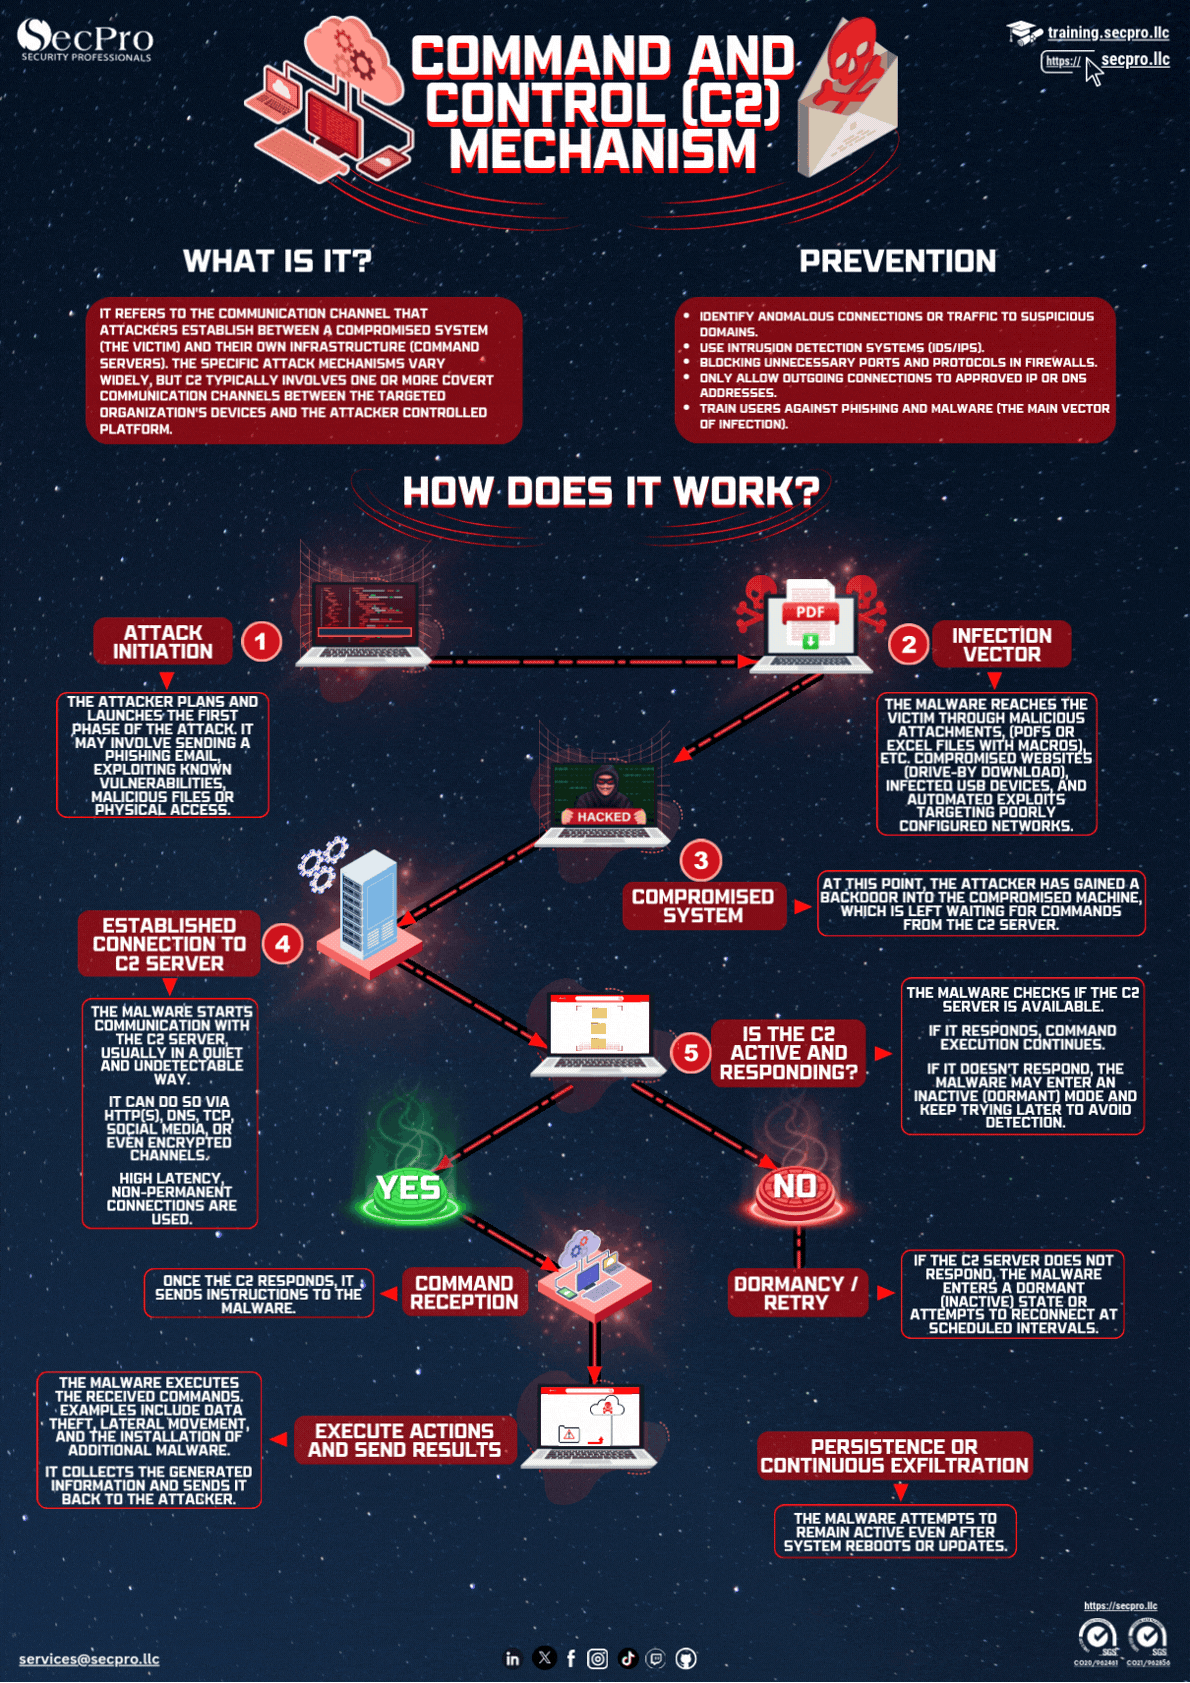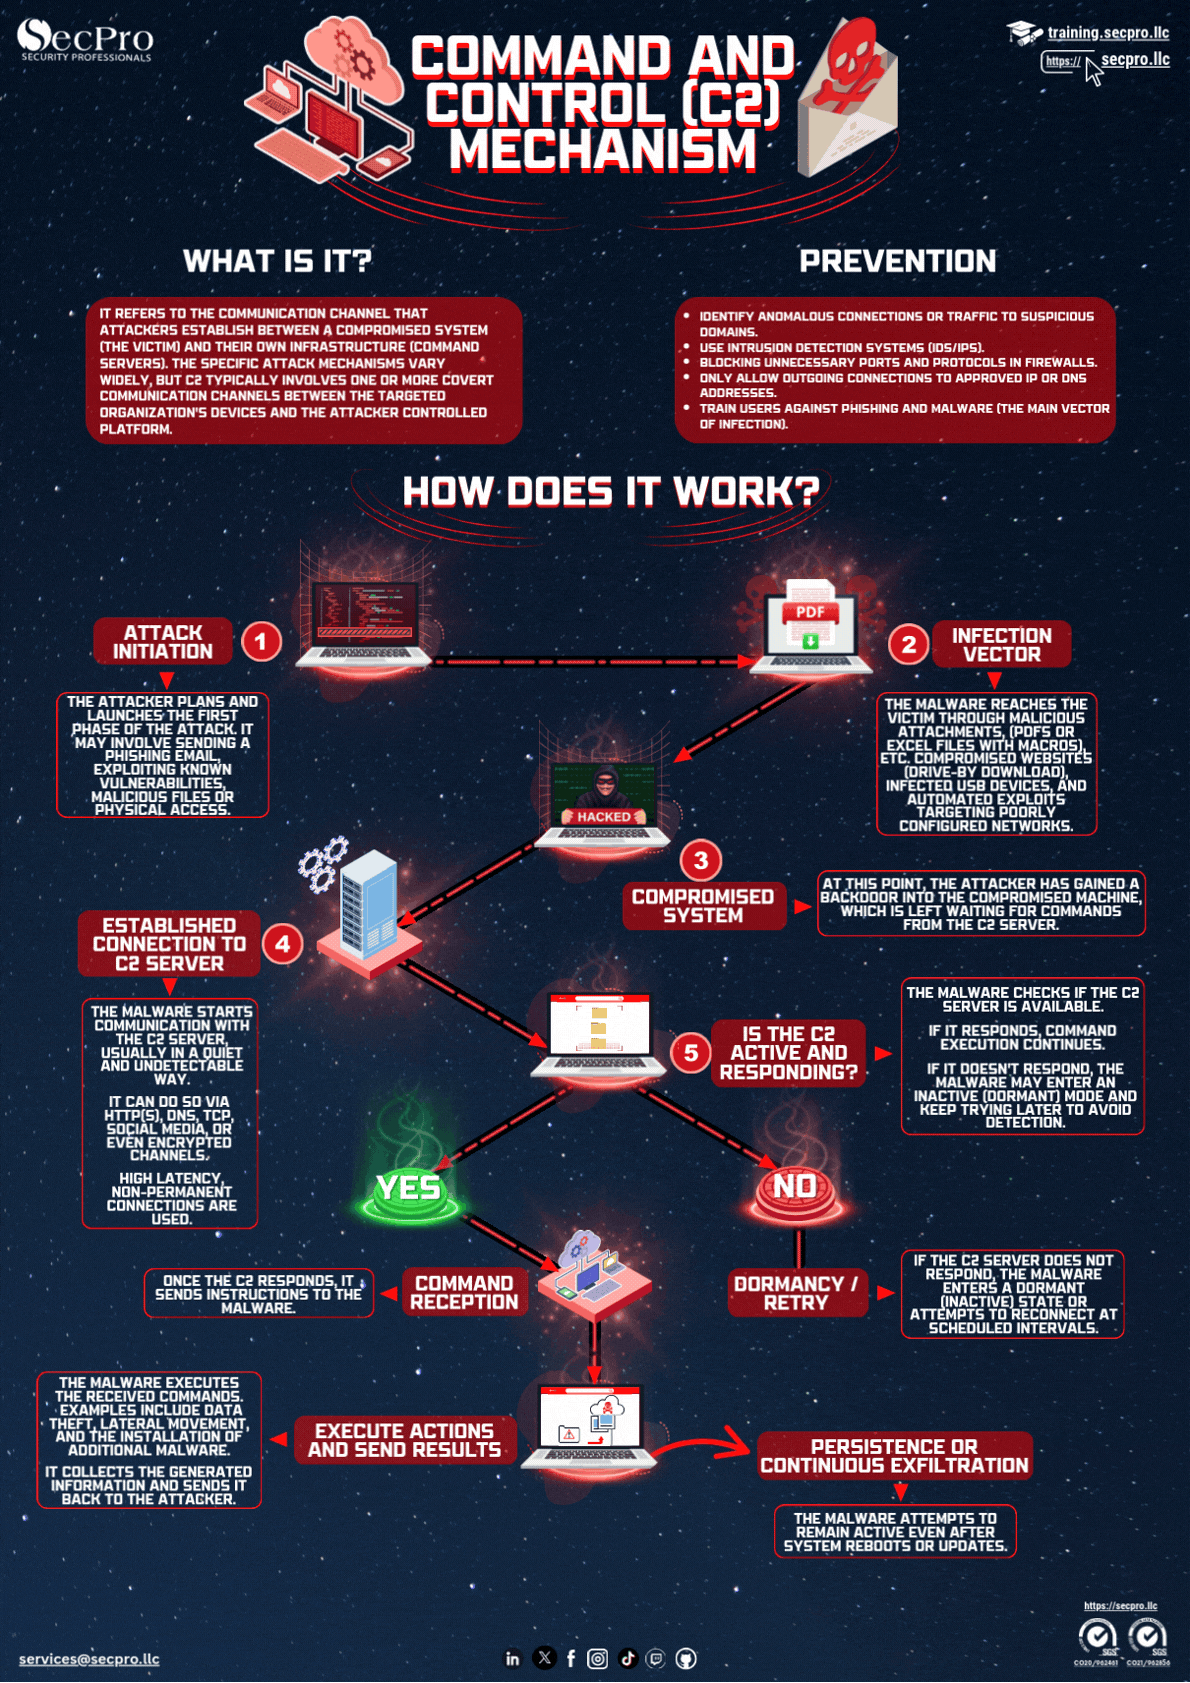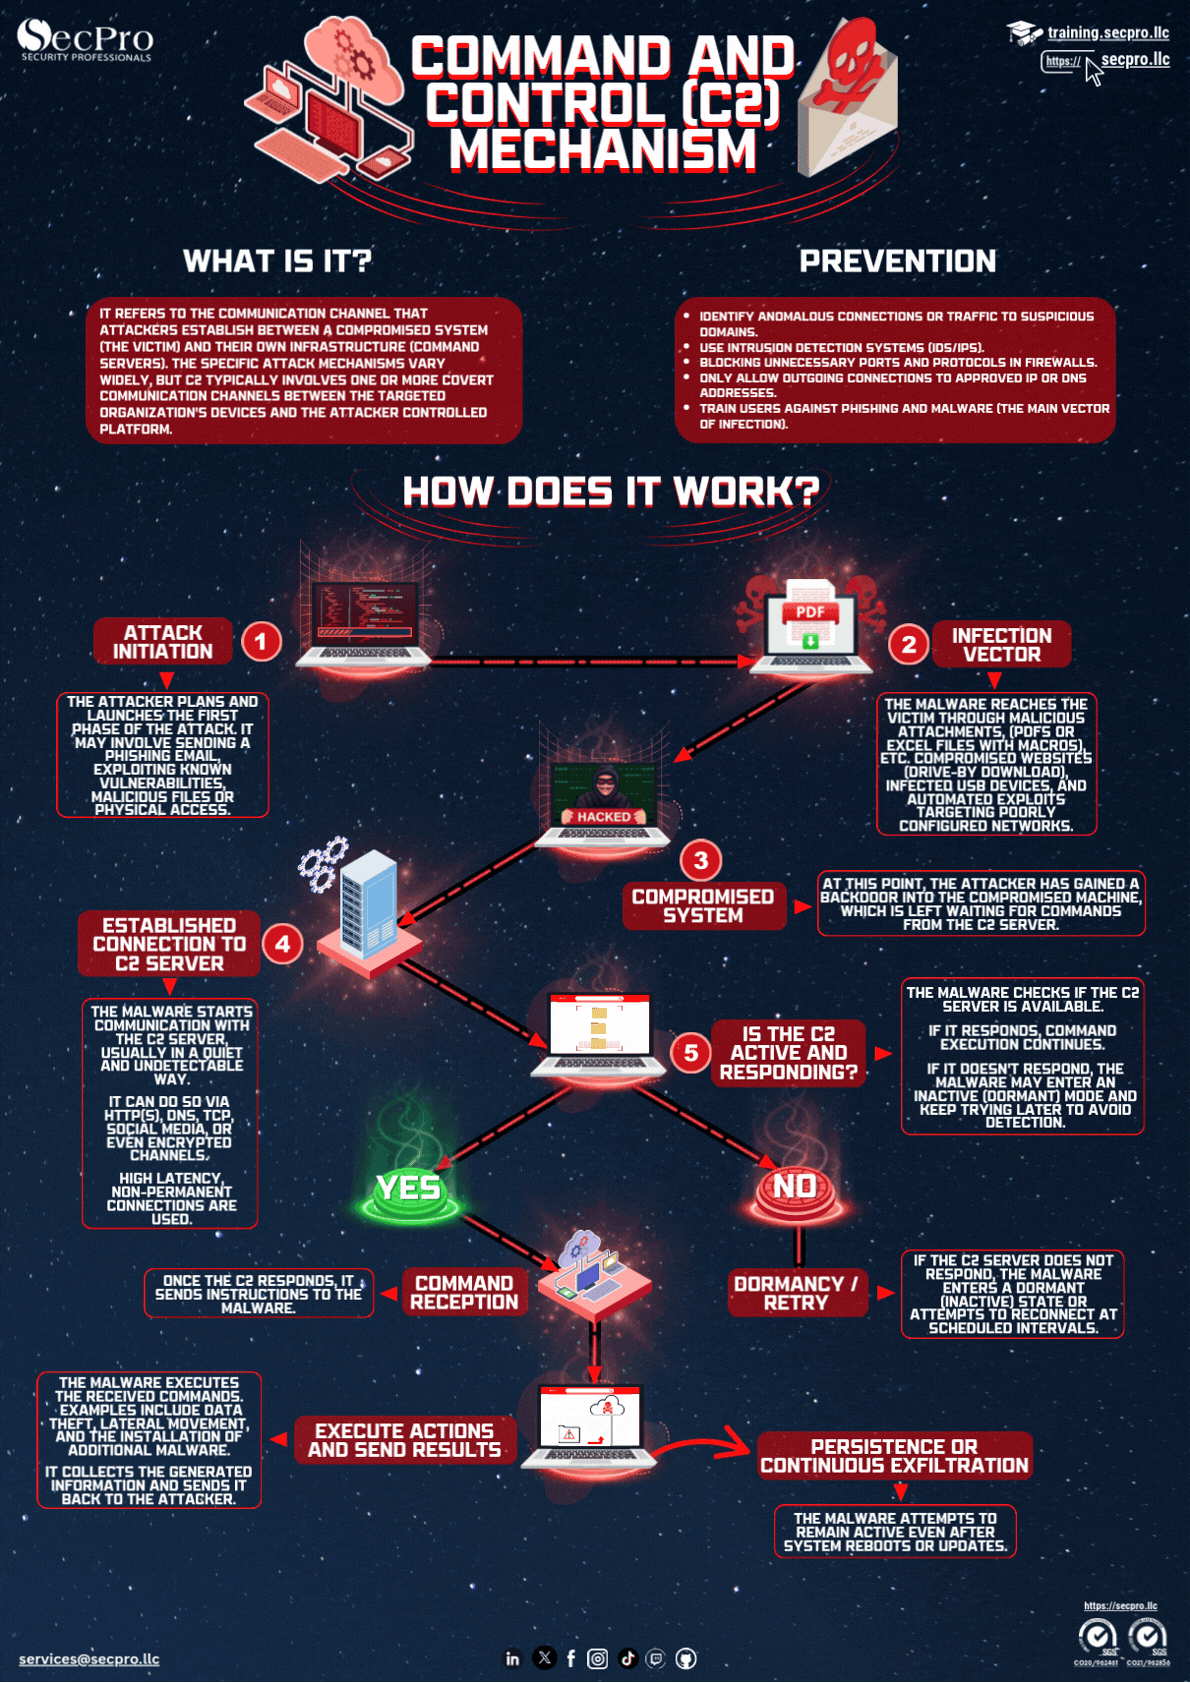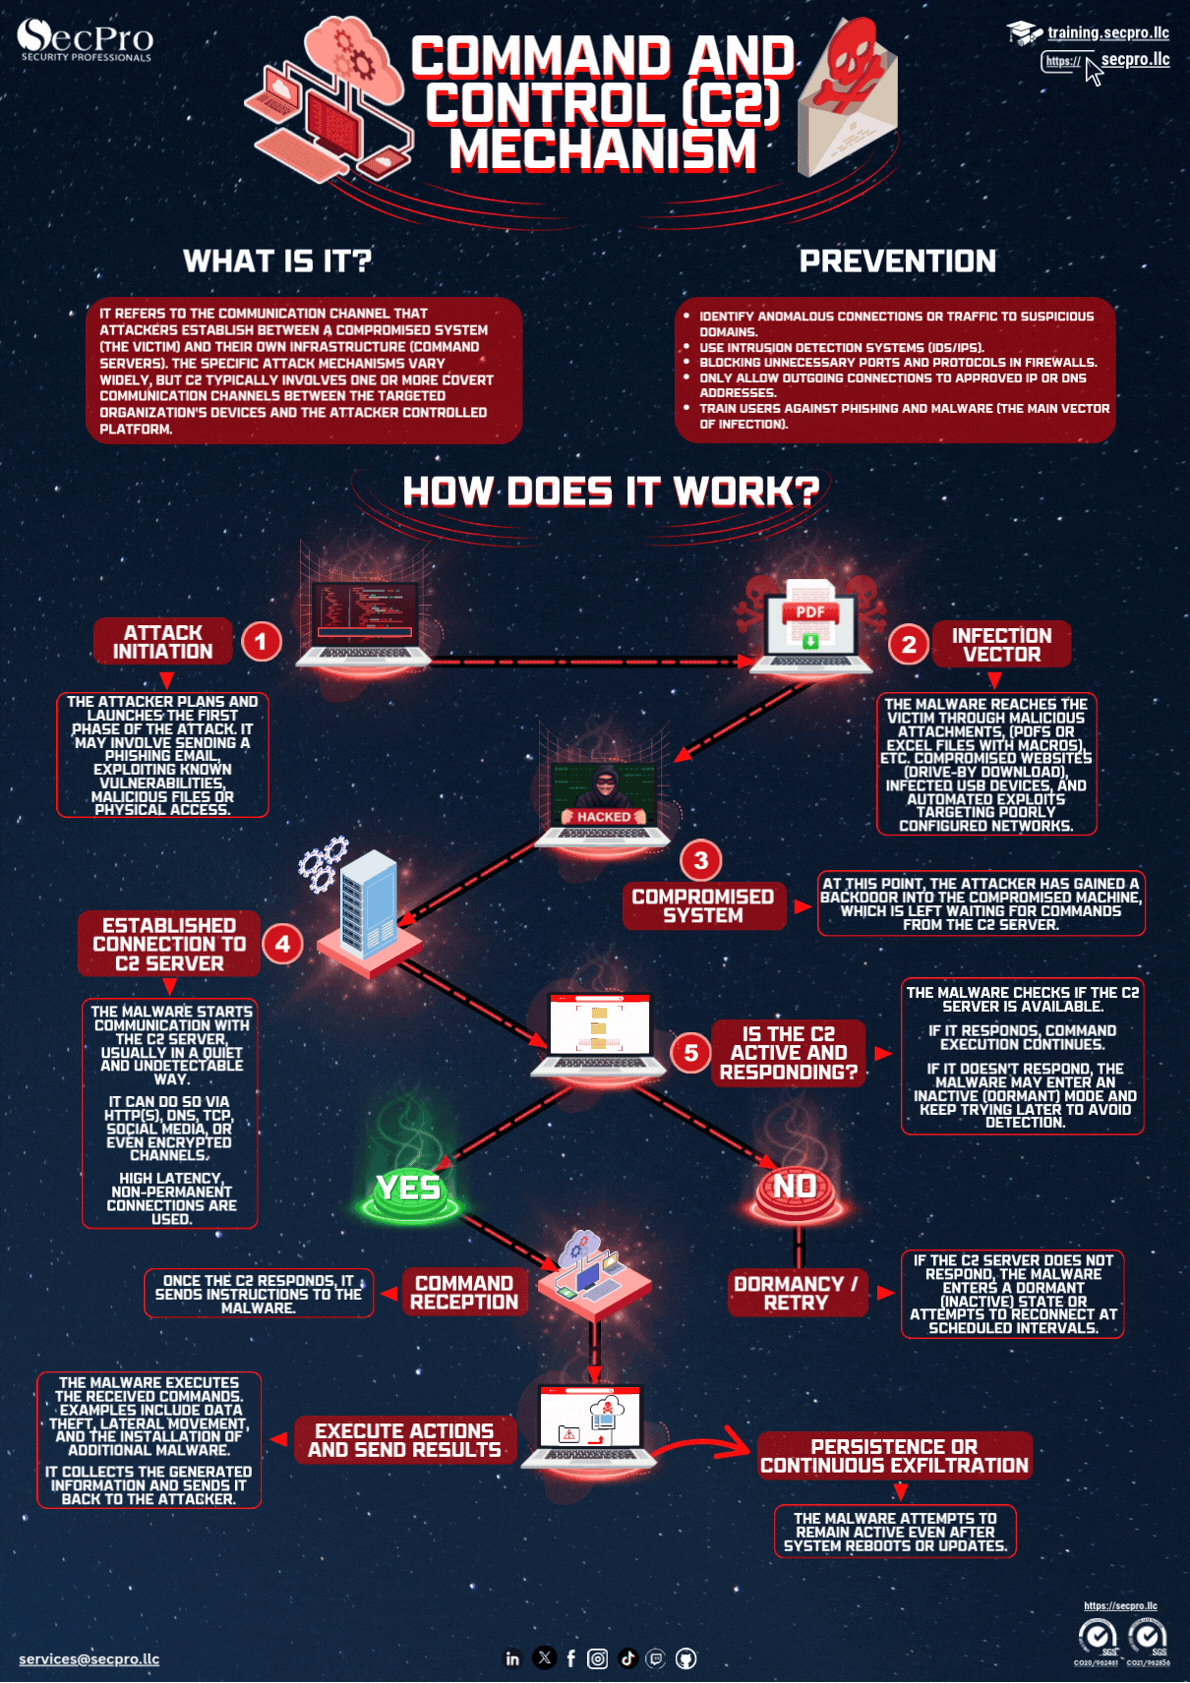
What is a command and control (C2) channel?
It is the path an attacker uses to stay in touch with the compromised machine: sending orders and receiving stolen data. Without C2, malware that already got in is isolated and loses almost all its usefulness, which is why cutting that channel is a priority in incident response.
How C2 communications are disguised
C2 traffic mimics legitimate traffic to blend in: HTTPS to reputable domains, DNS queries carrying encoded data, cloud services and social networks used as intermediaries, and beacons with randomized intervals so no regular, detectable pattern emerges.
How to detect C2 activity
Look for periodic connections to the same destination, anomalous DNS query volumes, freshly registered or low-reputation destinations, and encrypted traffic to locations unrelated to business operations. Network metadata analysis usually reveals the pattern even when the content is encrypted.