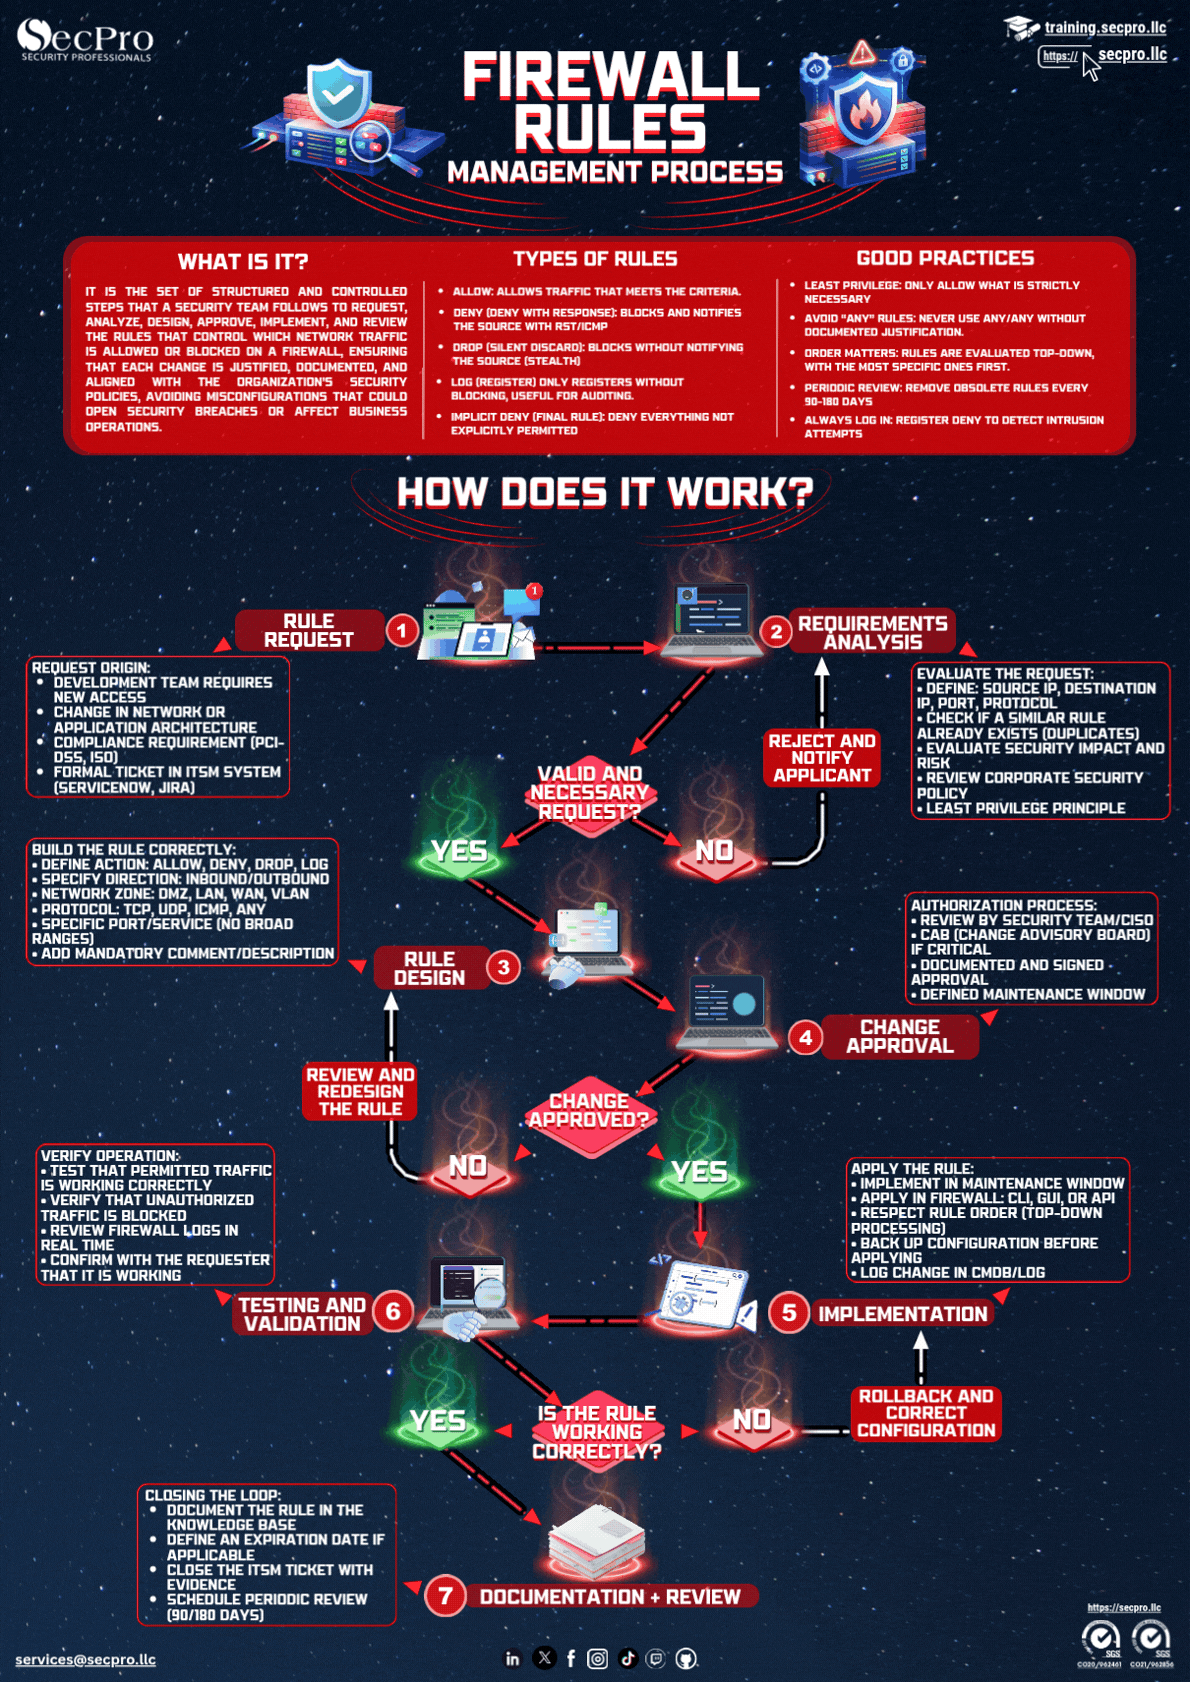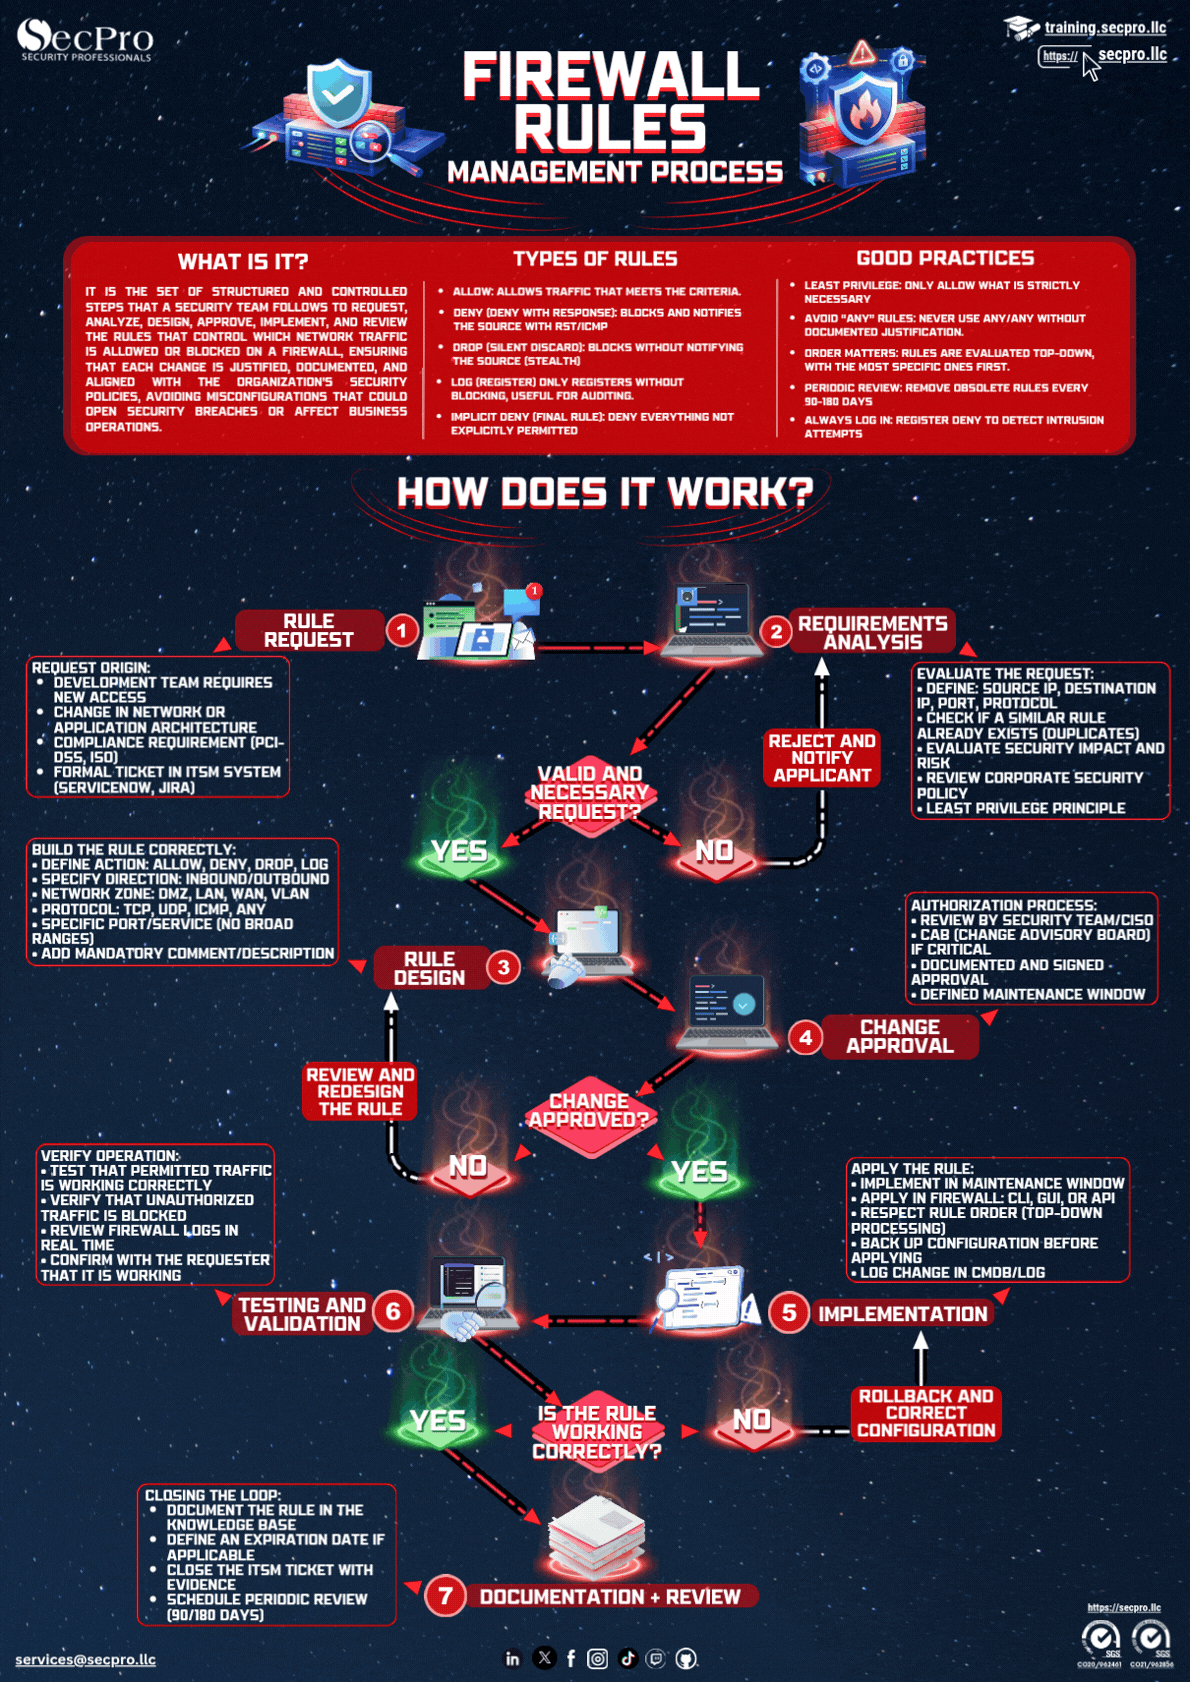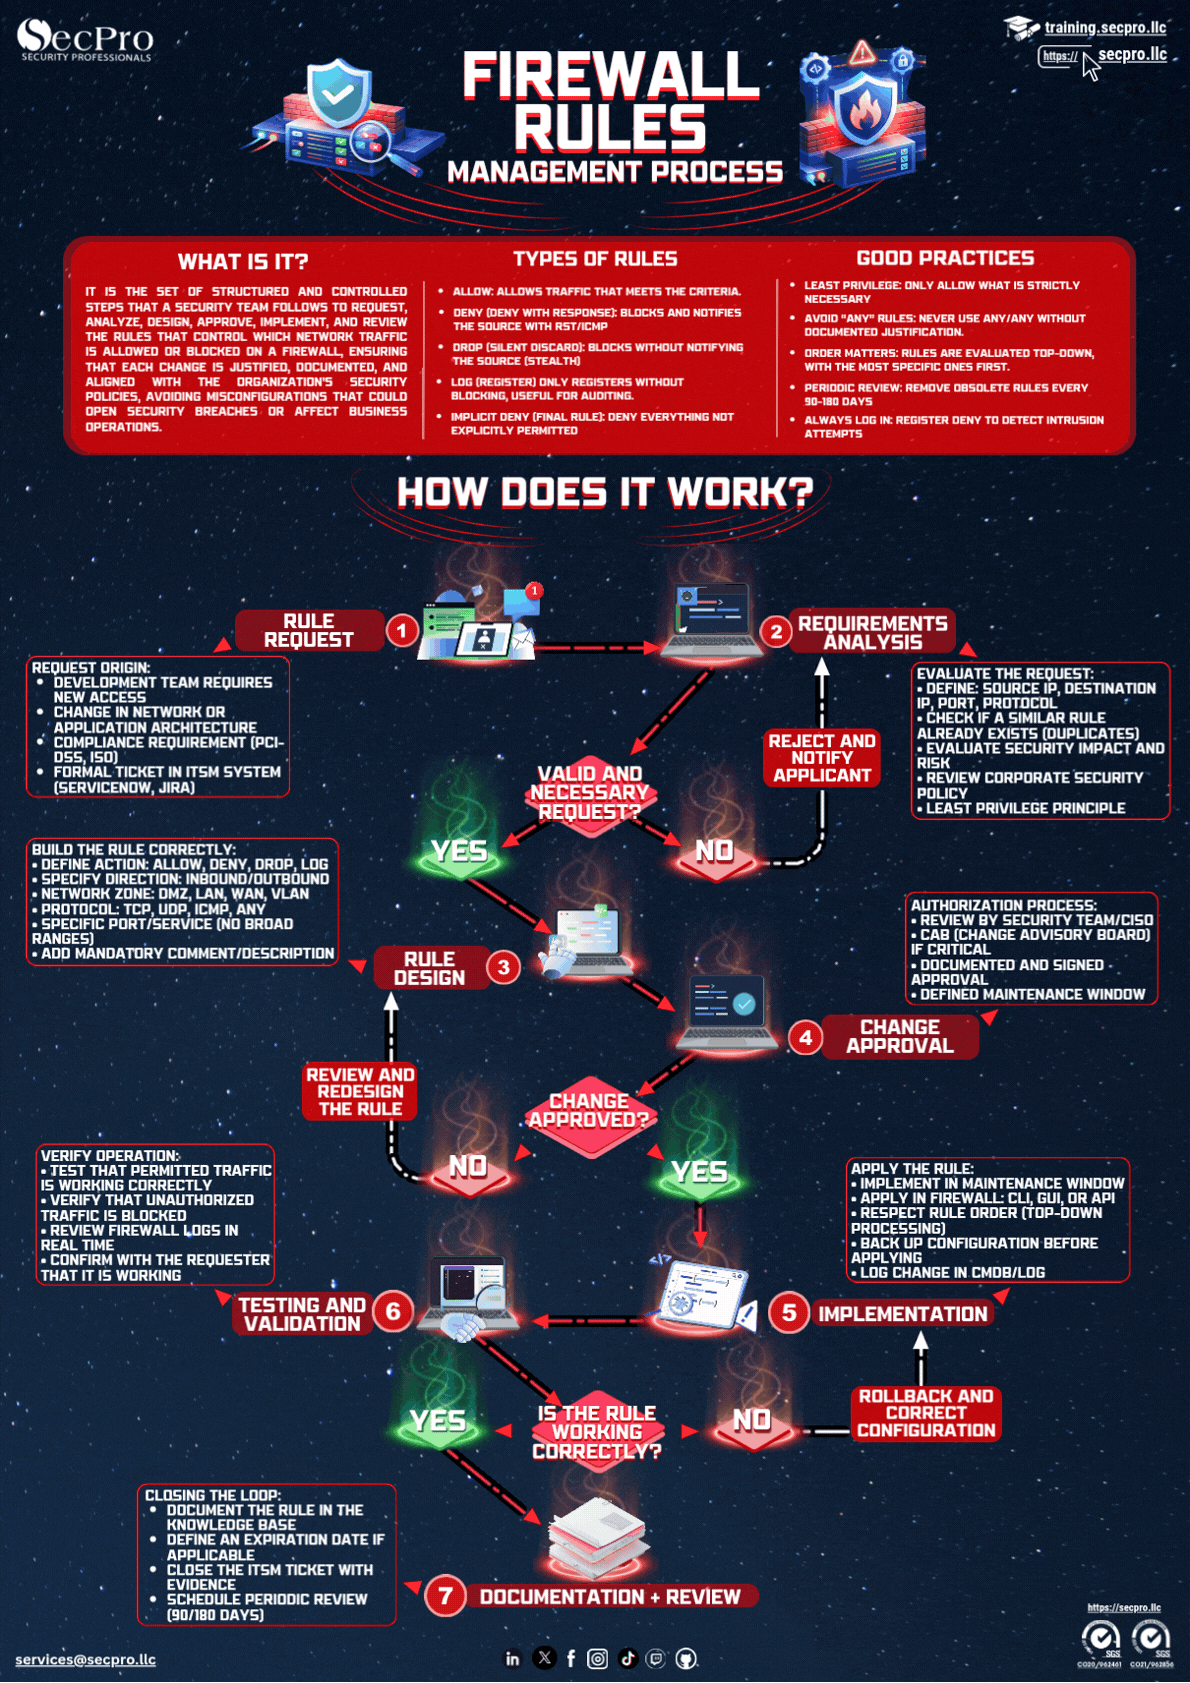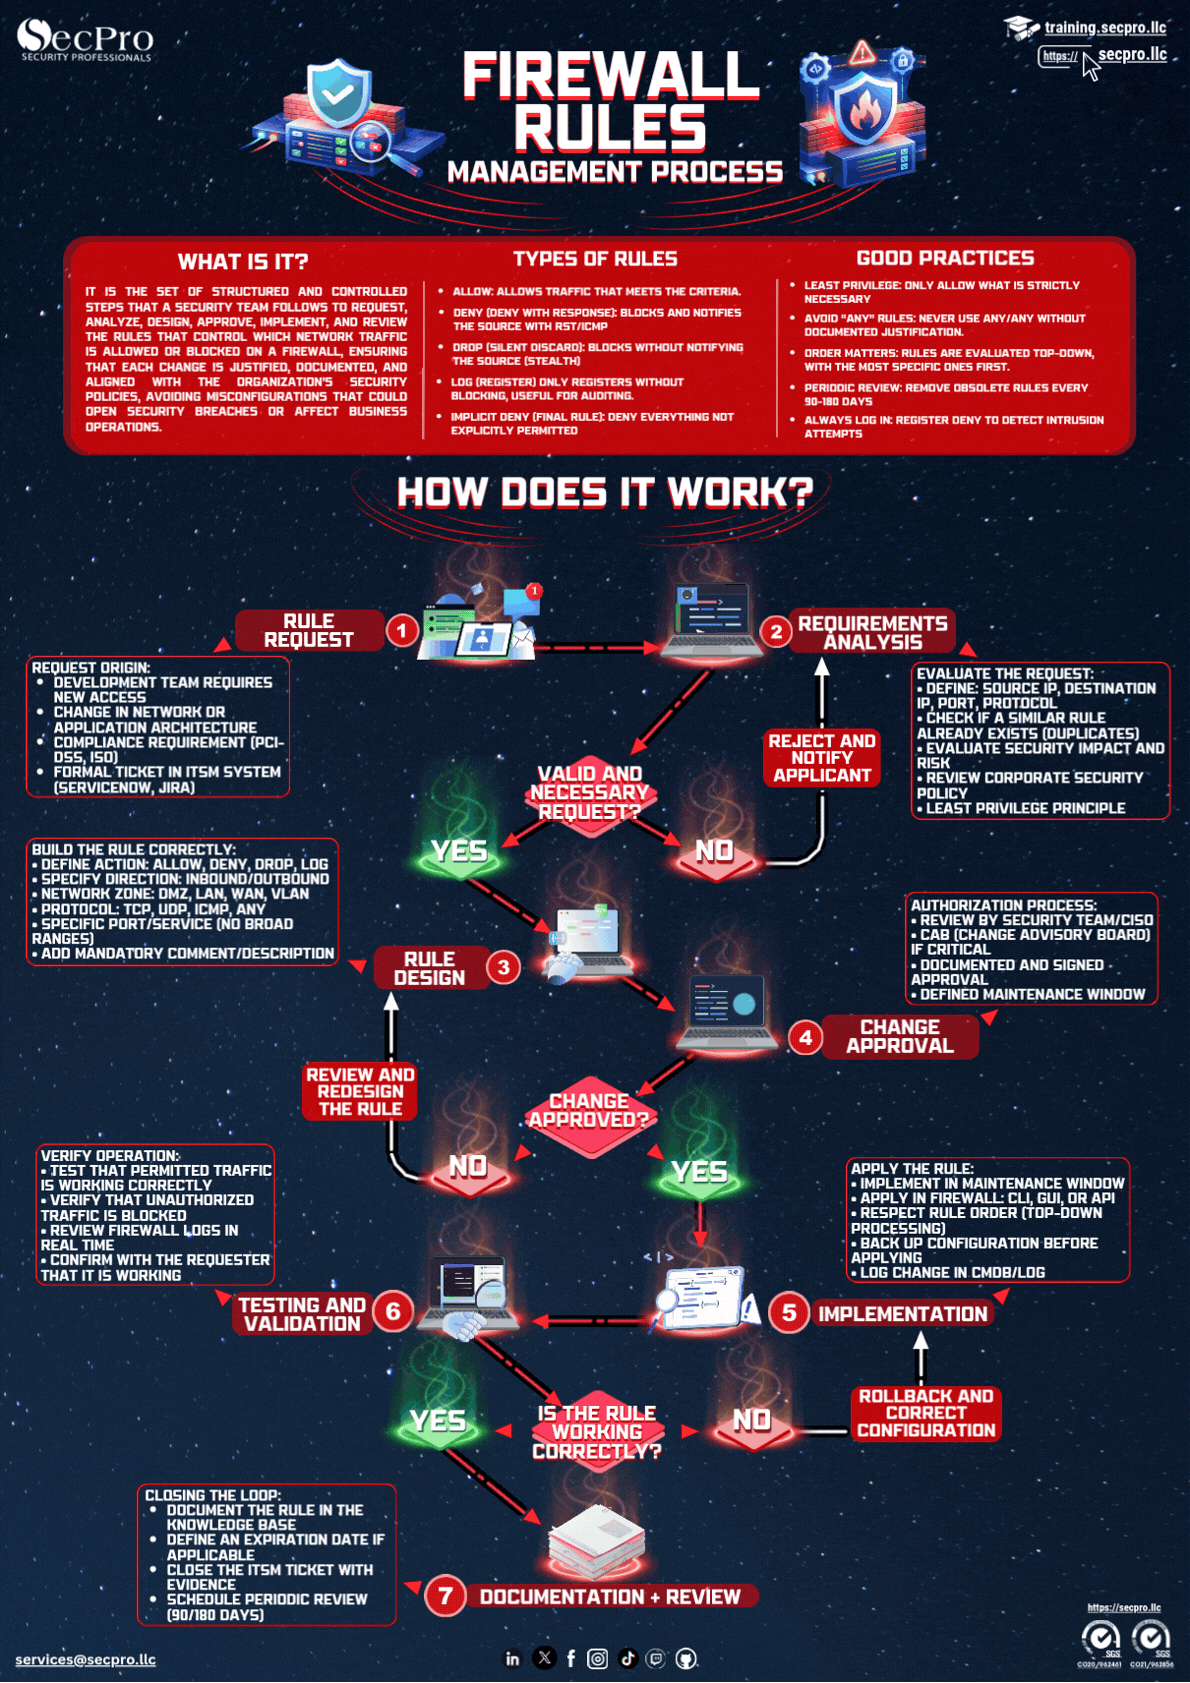
Why do firewall rule sets degrade?
A firewall accumulates rules over years: temporary exceptions never removed, permissions from closed projects, and objects pointing to decommissioned servers. The result is a contradictory set where broad rules placed early override the restrictive ones that follow, and nobody dares touch it for fear of breaking production.
What a rule audit reviews
Duplicate, shadowed (never evaluated because another rule precedes them) and overly permissive rules, especially those using any in source, destination or service. Also evaluation order, orphaned objects, rules with no activity logged for months, and the absence of an explicit deny rule at the end.
Management best practices
Apply least privilege with specific rules, document each one with an owner, purpose and expiry date, require a formal change process, periodically review real usage, and remove what is unused. A clean rule base is not only safer: it is also far faster to diagnose during an incident.