What is penetration testing?
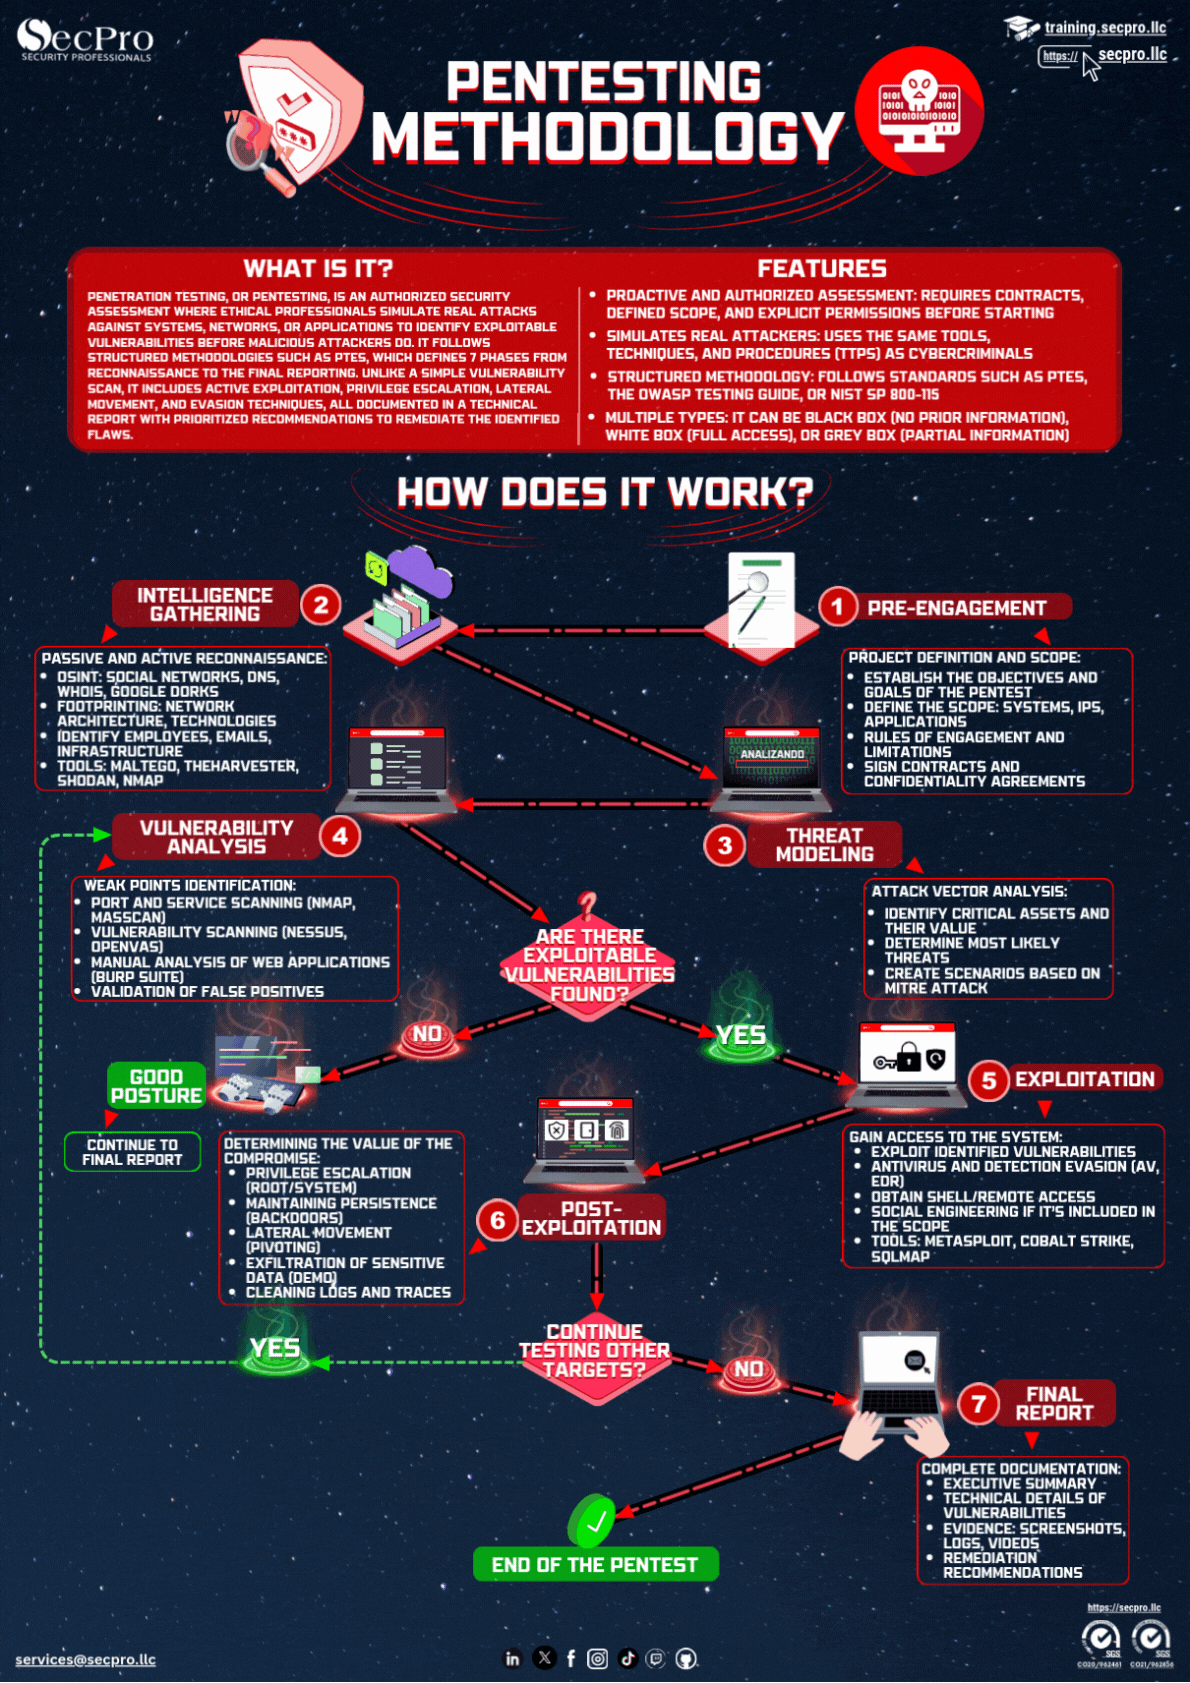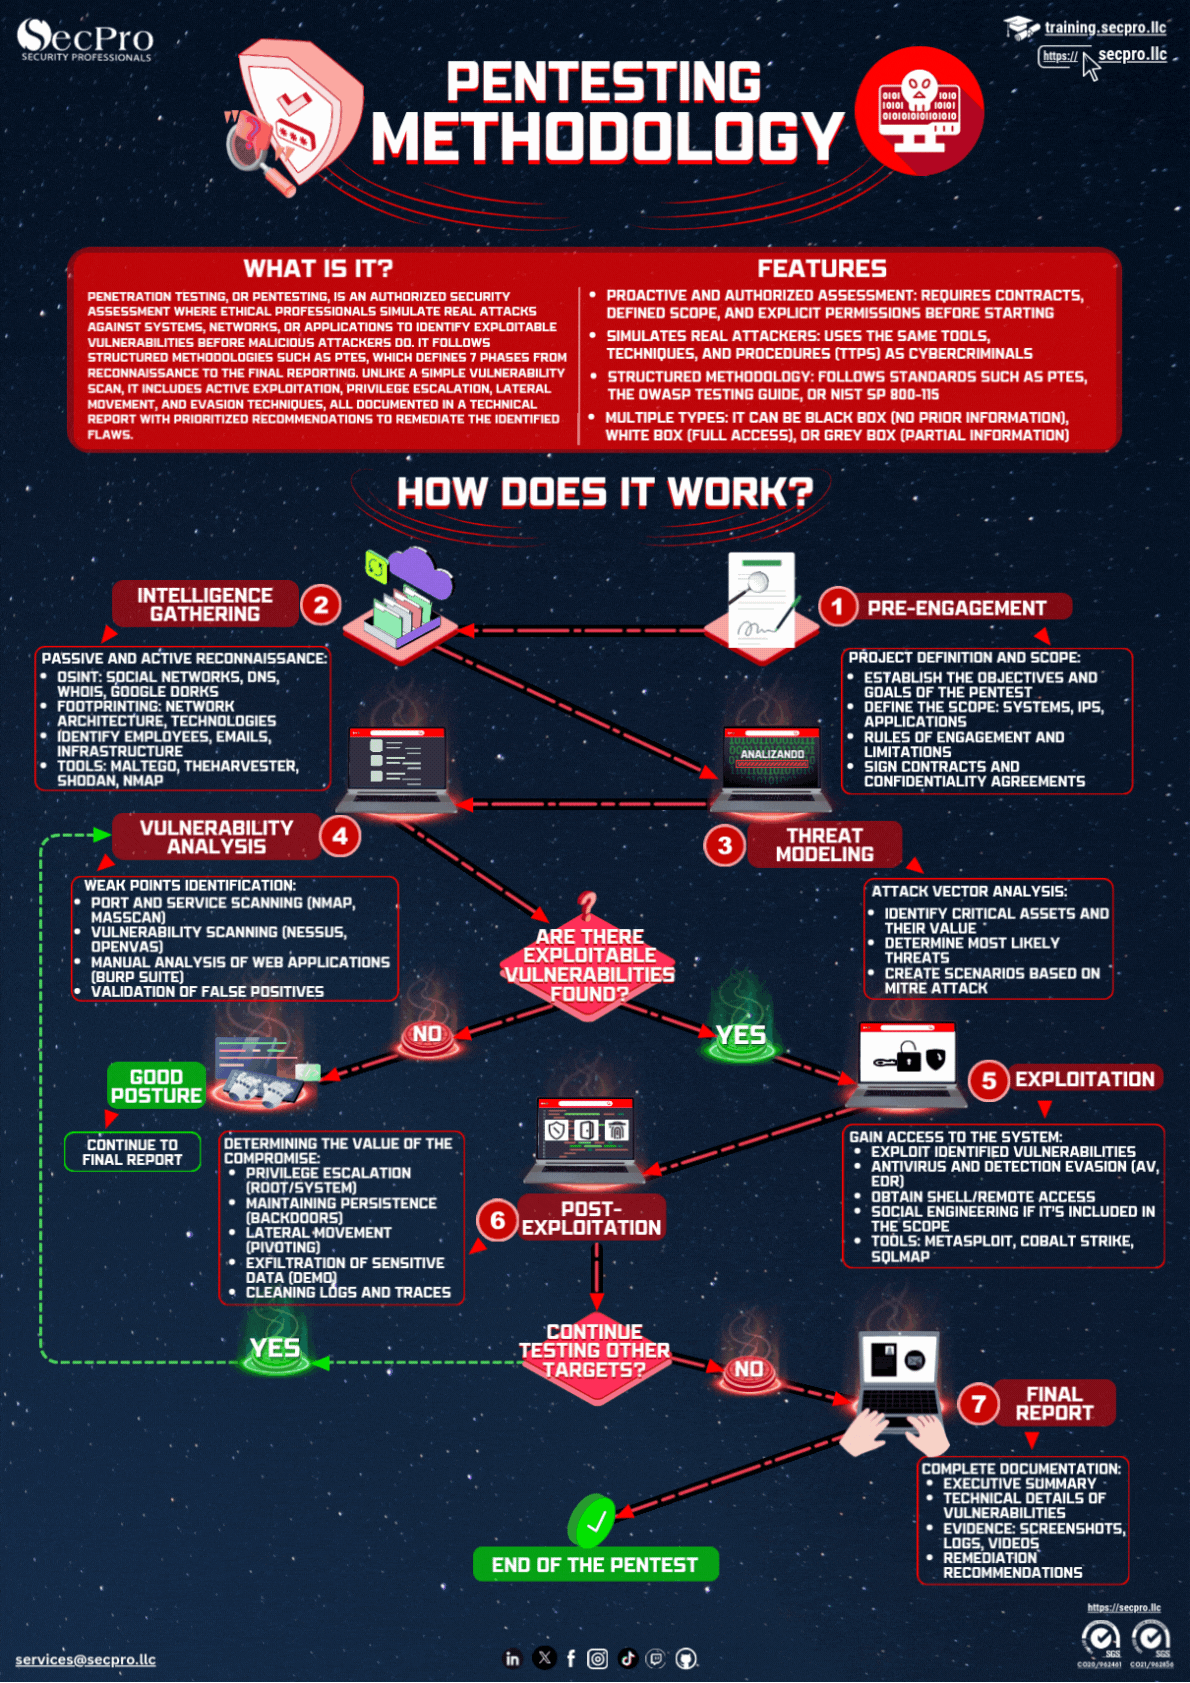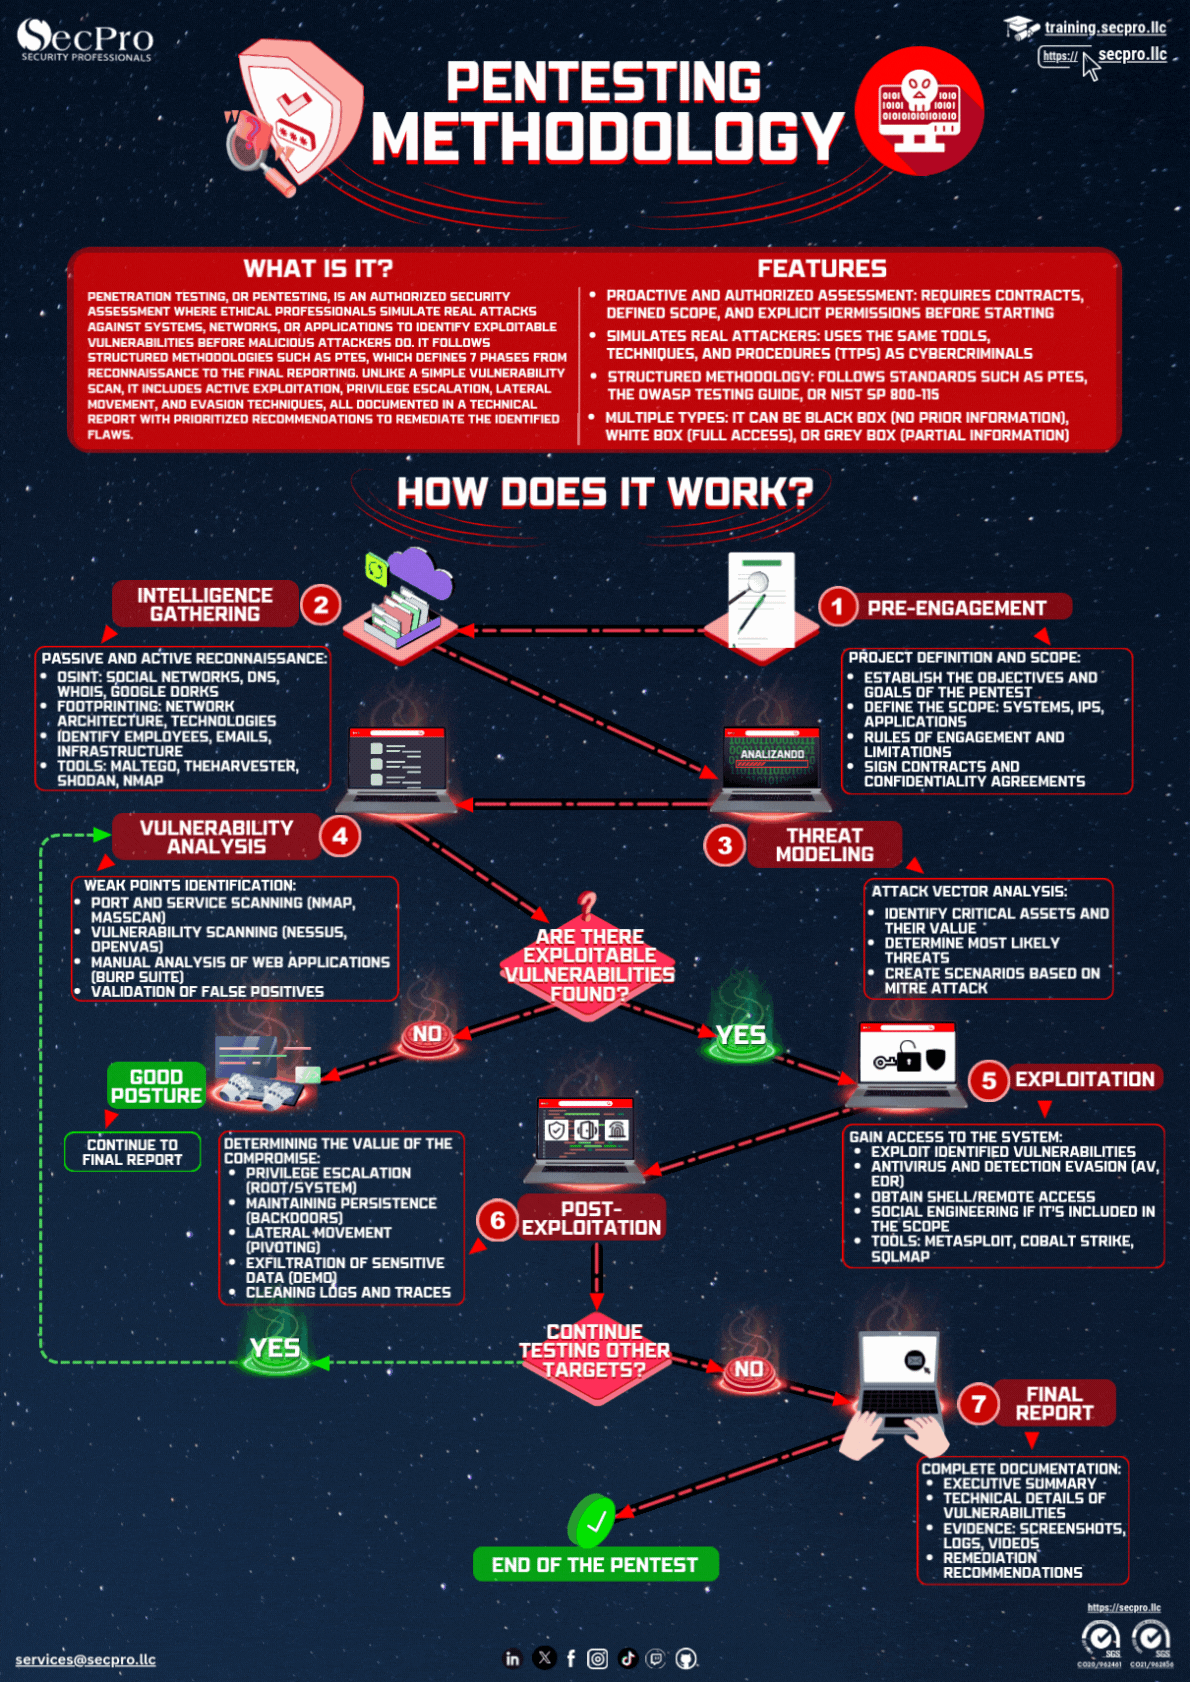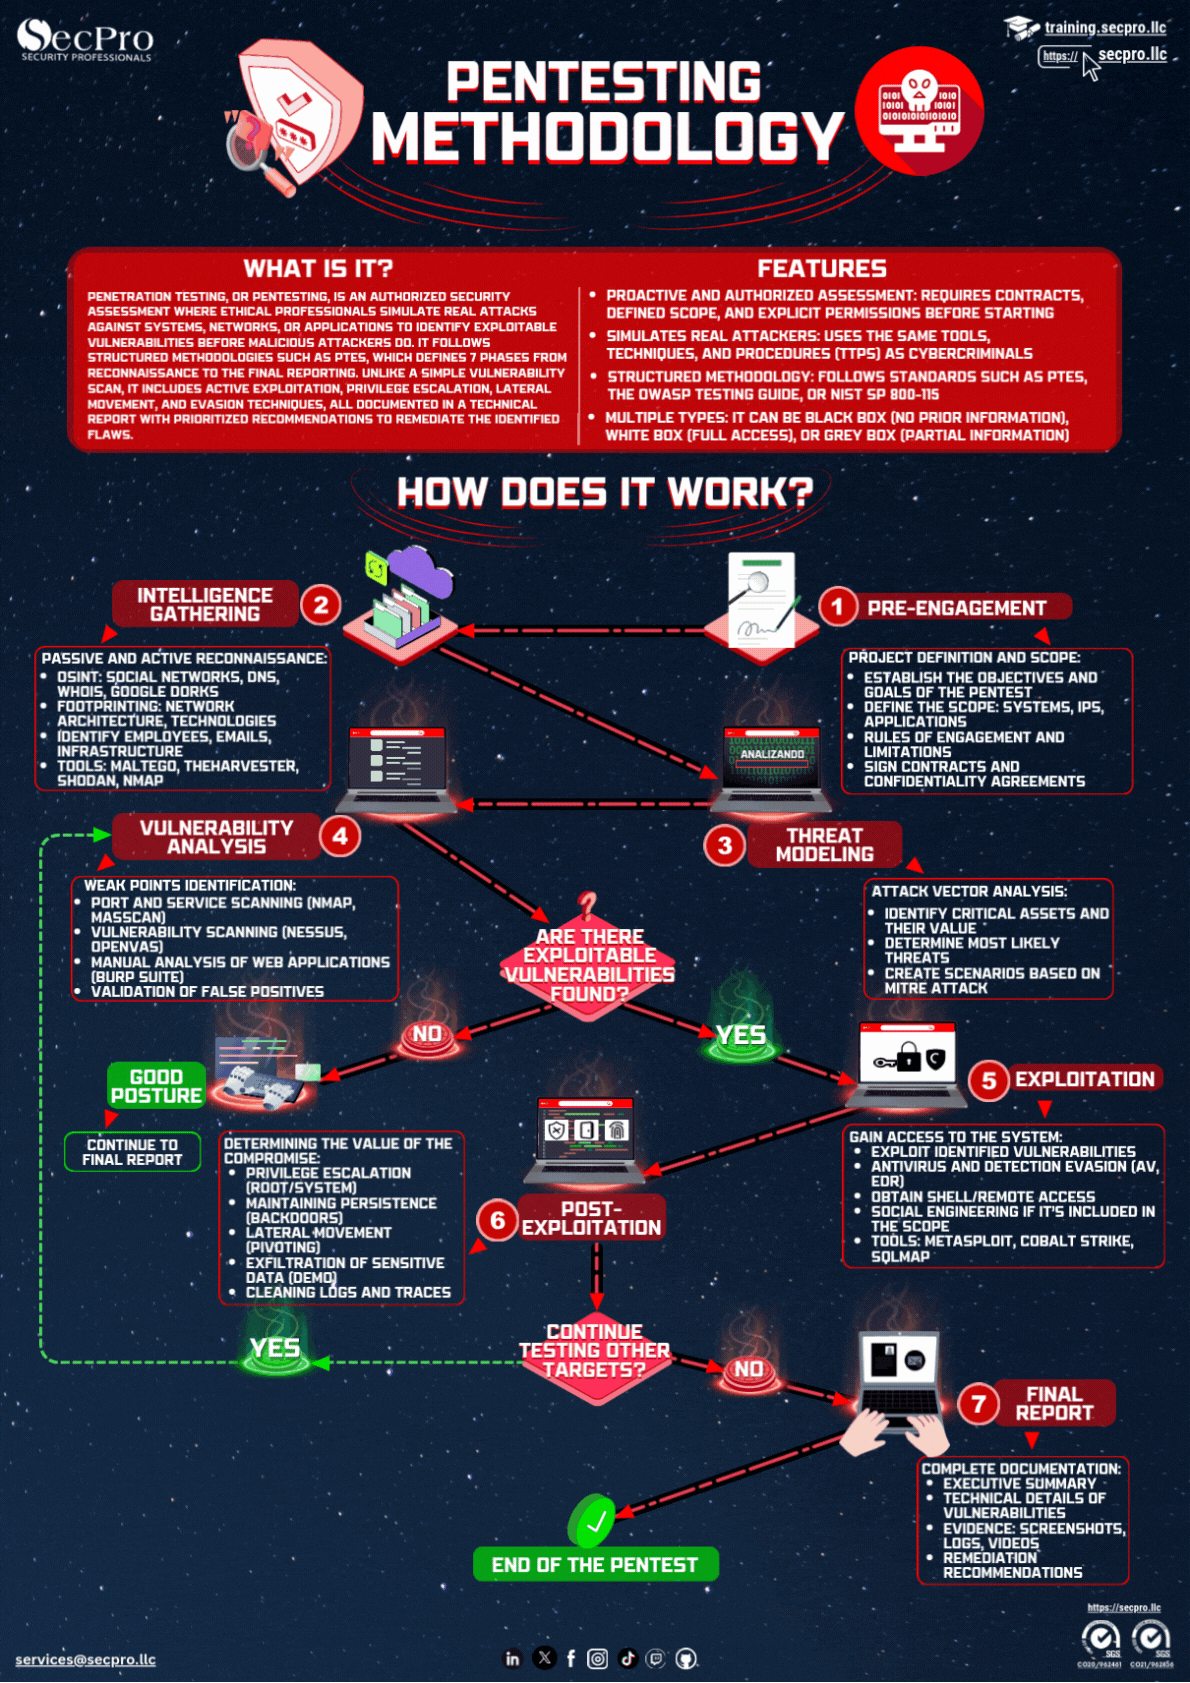
A penetration test is an authorized simulated attack against a system to find and exploit its weaknesses before a real attacker does. It goes beyond listing vulnerabilities: it exploits them under control to demonstrate the concrete impact they would have on the business.
Phases of a penetration test
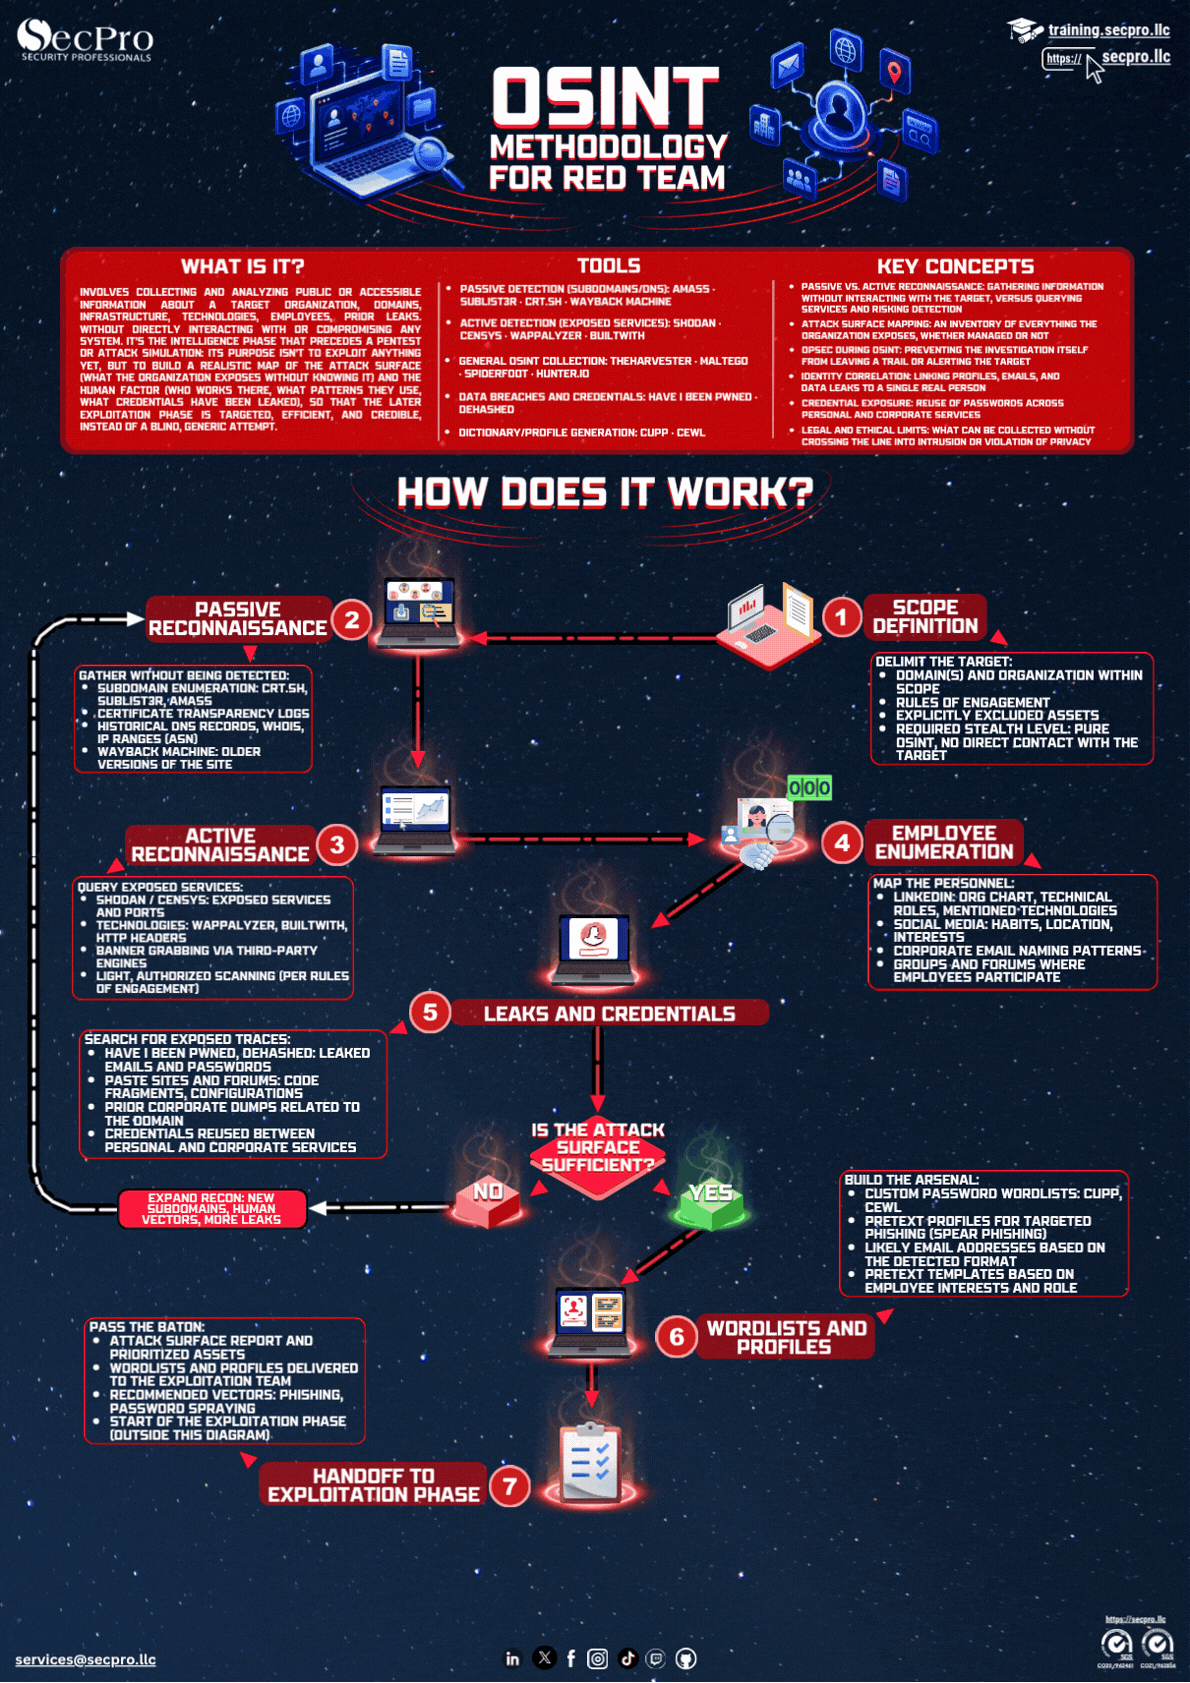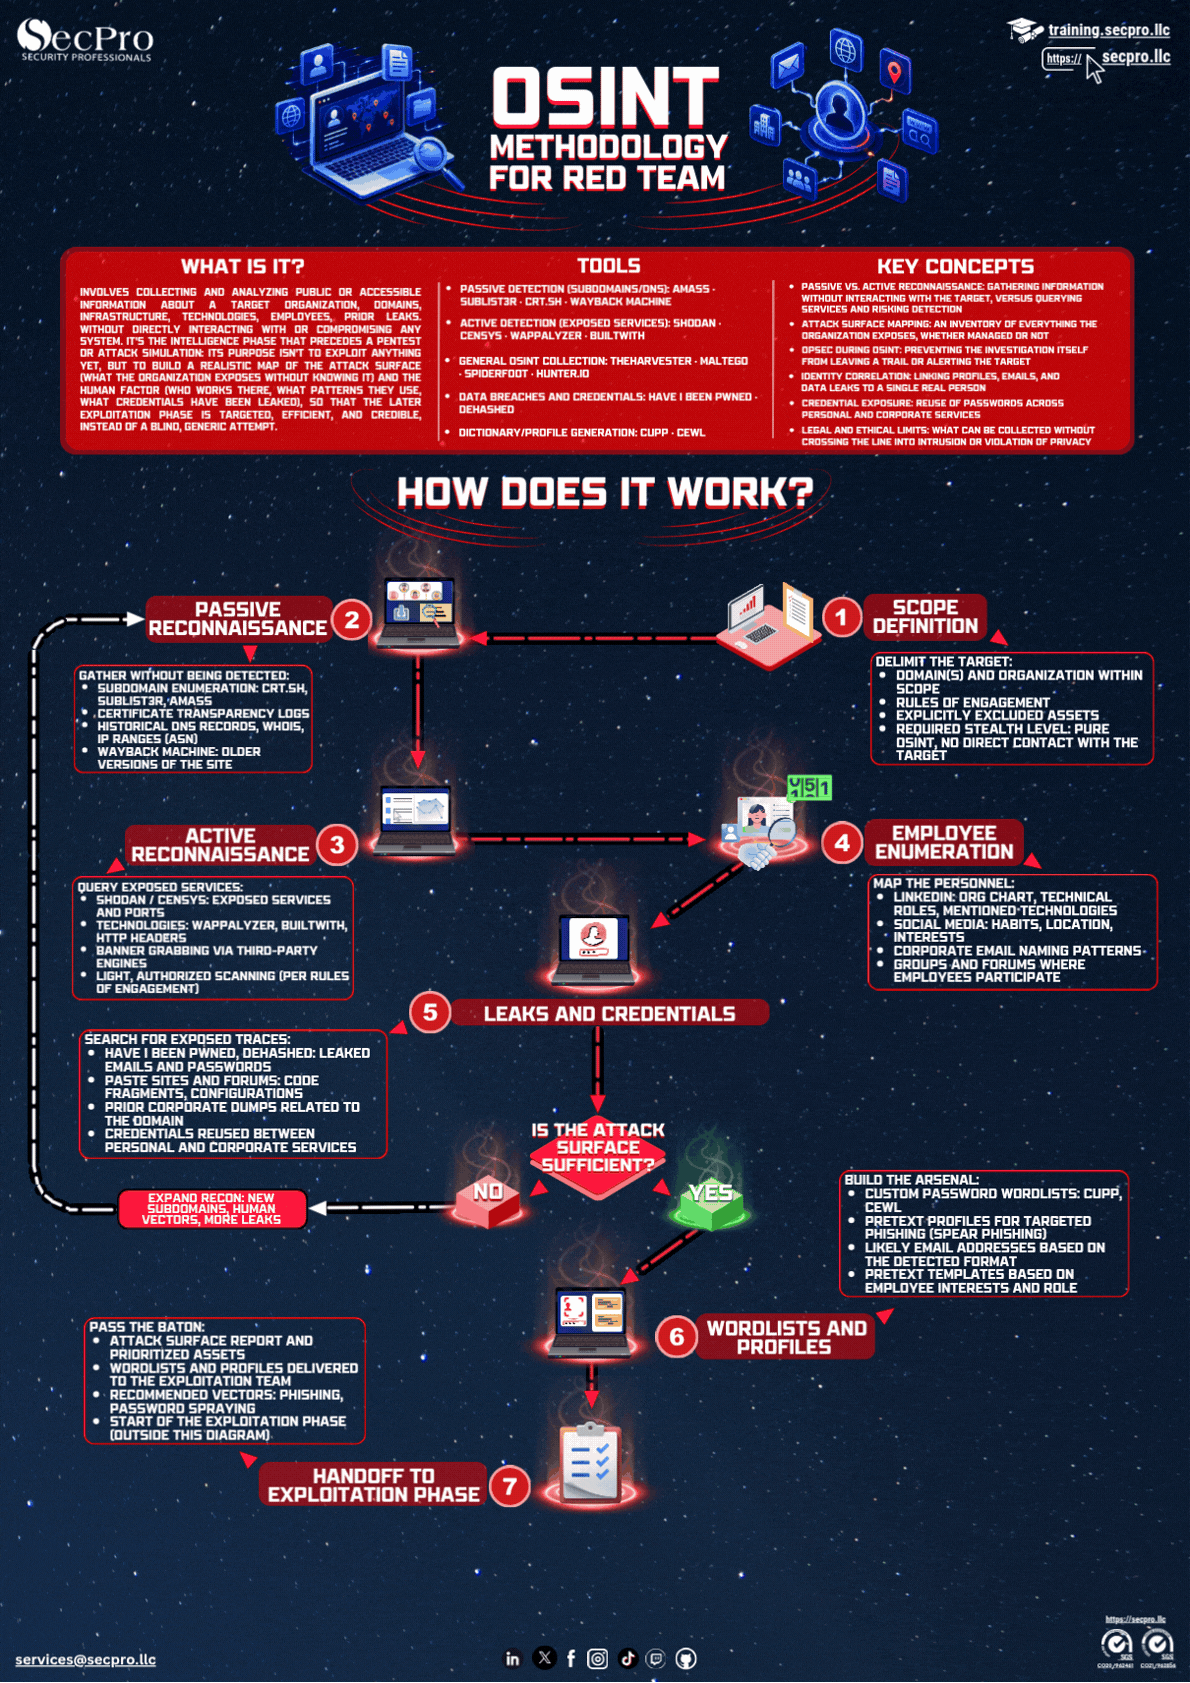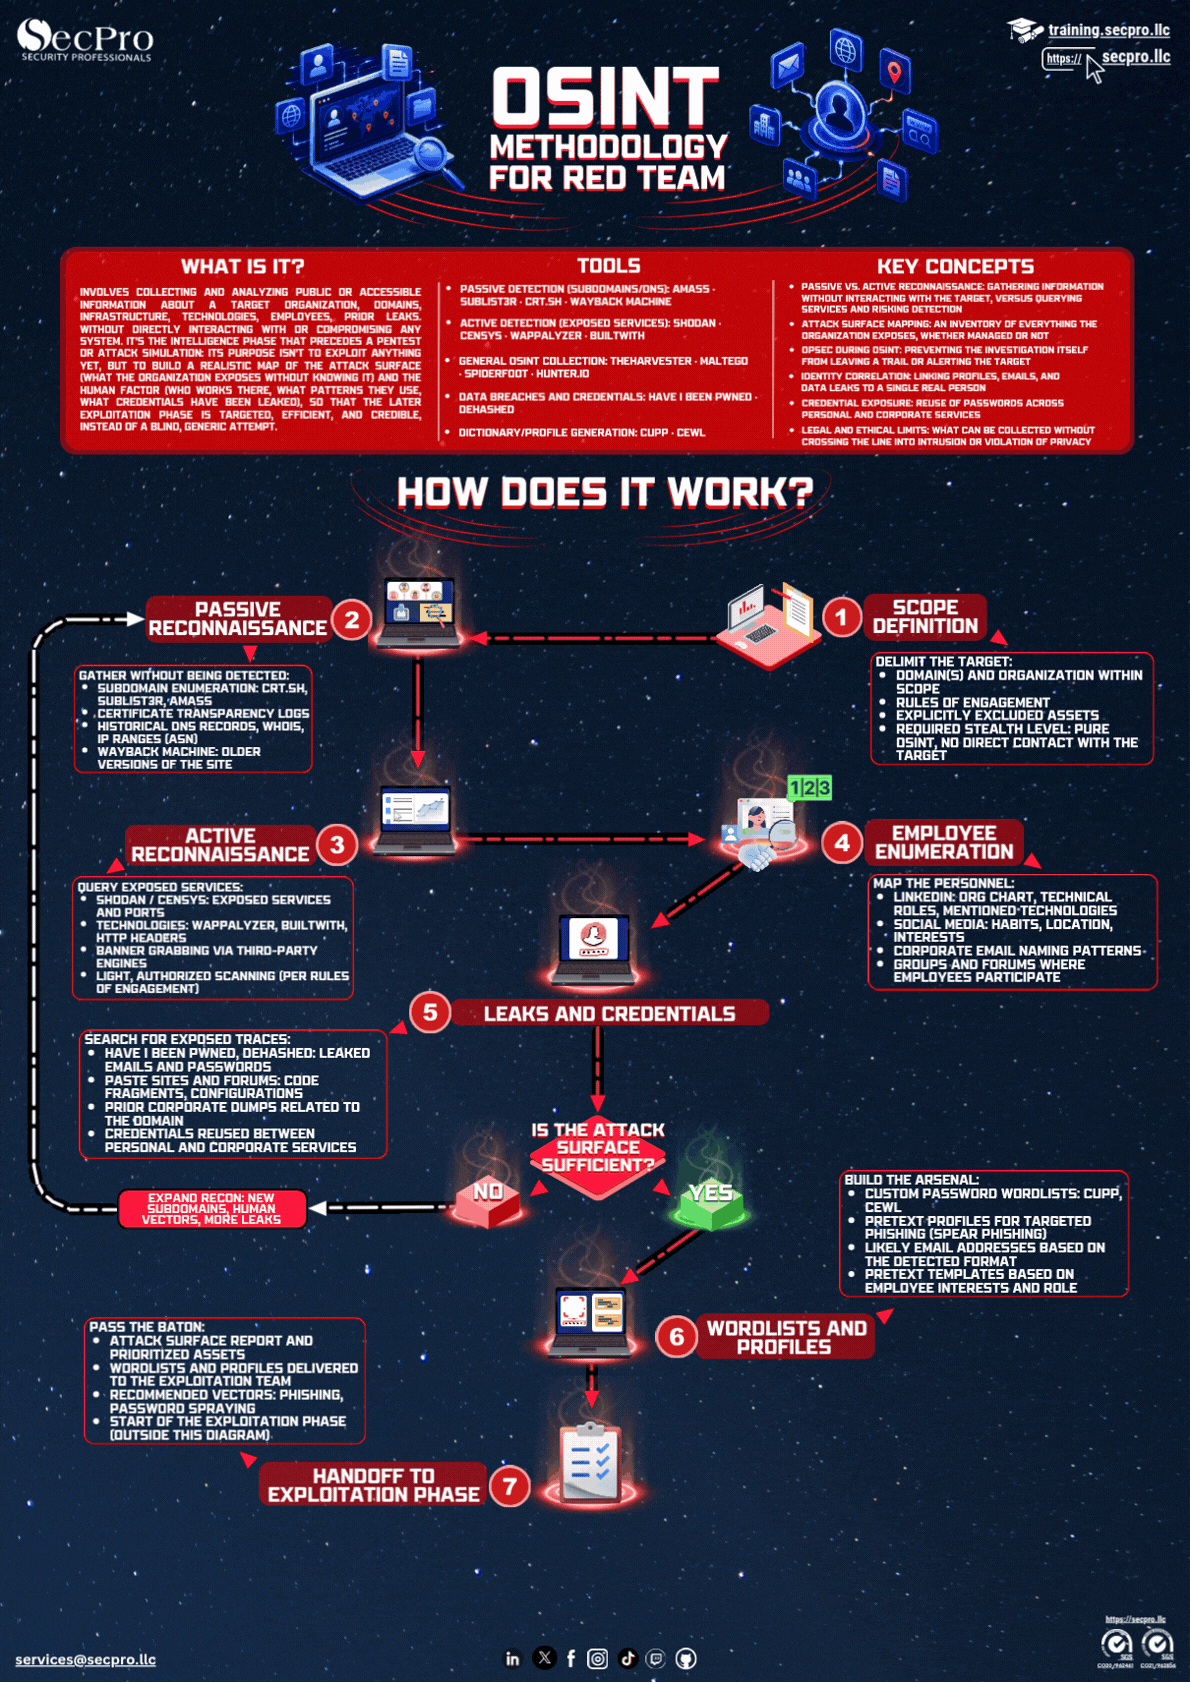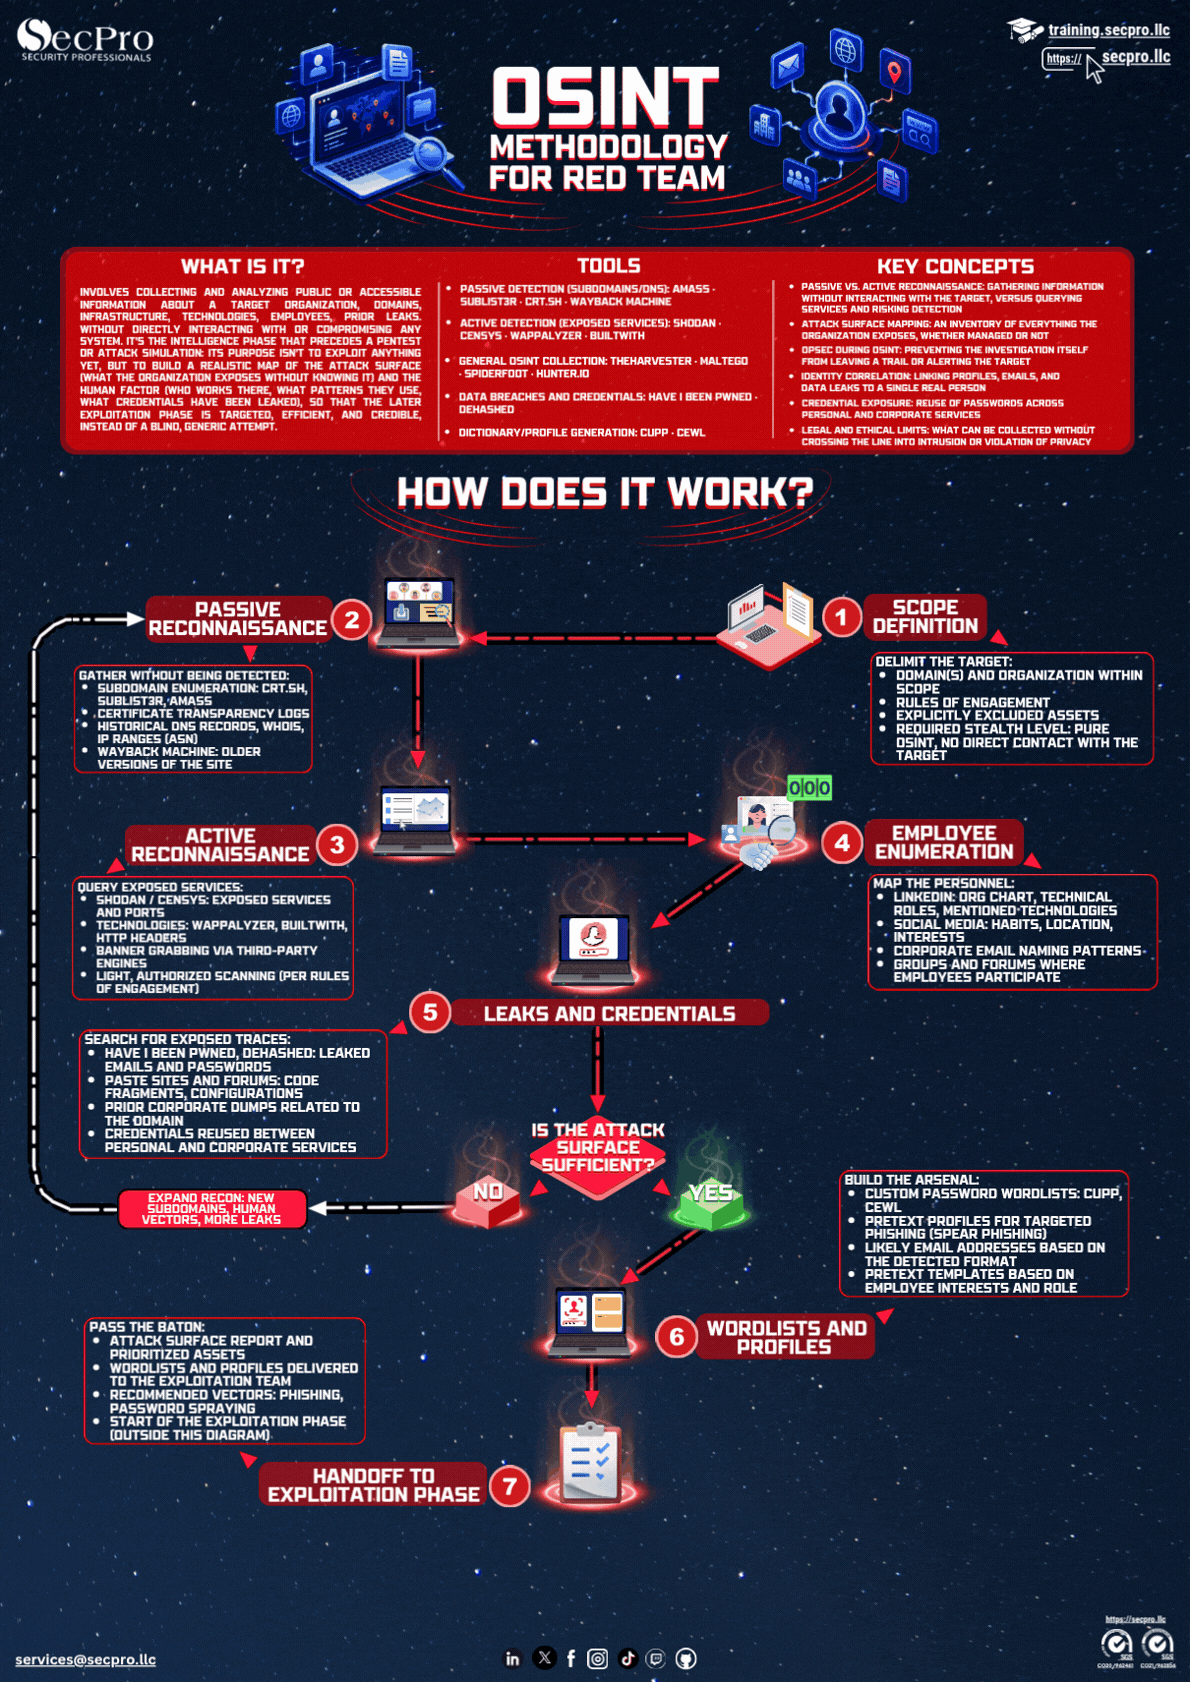
Reconnaissance and information gathering; scanning and identification of services and vulnerabilities; exploitation to gain access; post-exploitation, where real reach is assessed through privilege escalation and lateral movement; and finally the report with findings, evidence, severity and remediation guidance.
Black, grey and white box
In black box the team starts with no information, like an external attacker. In grey box it holds credentials or partial documentation, simulating a user or an attacker who already gained access. In white box it has full access including source code, offering the broadest coverage per unit of time invested.